 Customer Hub
APNS Push Certificates
To communicate with Apple devices via MDM, Relution requires a signed APNS push certificate (Apple Push Notification service). This certificate is linked to an Apple Account and must be renewed before it expires.
If a certificate expires, all enrolled Apple devices lose their MDM connection and must be re-enrolled.
As long as no APNS certificate is in effect for an organization, no iOS, macOS or tvOS devices can be enrolled: these platforms are disabled when creating an enrollment, and the tooltip refers to Settings → Organization Certificates. In addition, the entry APNS certificate missing appears under Notifications with the link Set up certificate, which leads directly to that page.
Migration from the Previous Process
New in 26.3If the Relution installation was set up prior to version 26.3.0 and a certificate was previously provided by sending a CSR to Relution Support, a one-time migration must be performed before using the Self-Service Wizard.
The migration takes place under Settings → Organization Certificates. If a migration is available for the organization, an information box appears, followed by the entry Migrate your old APNS certificate with the Migrate button. Clicking it starts the migration. No migration is offered in the global organization and in meta-organizations, as the previous process was never available there.
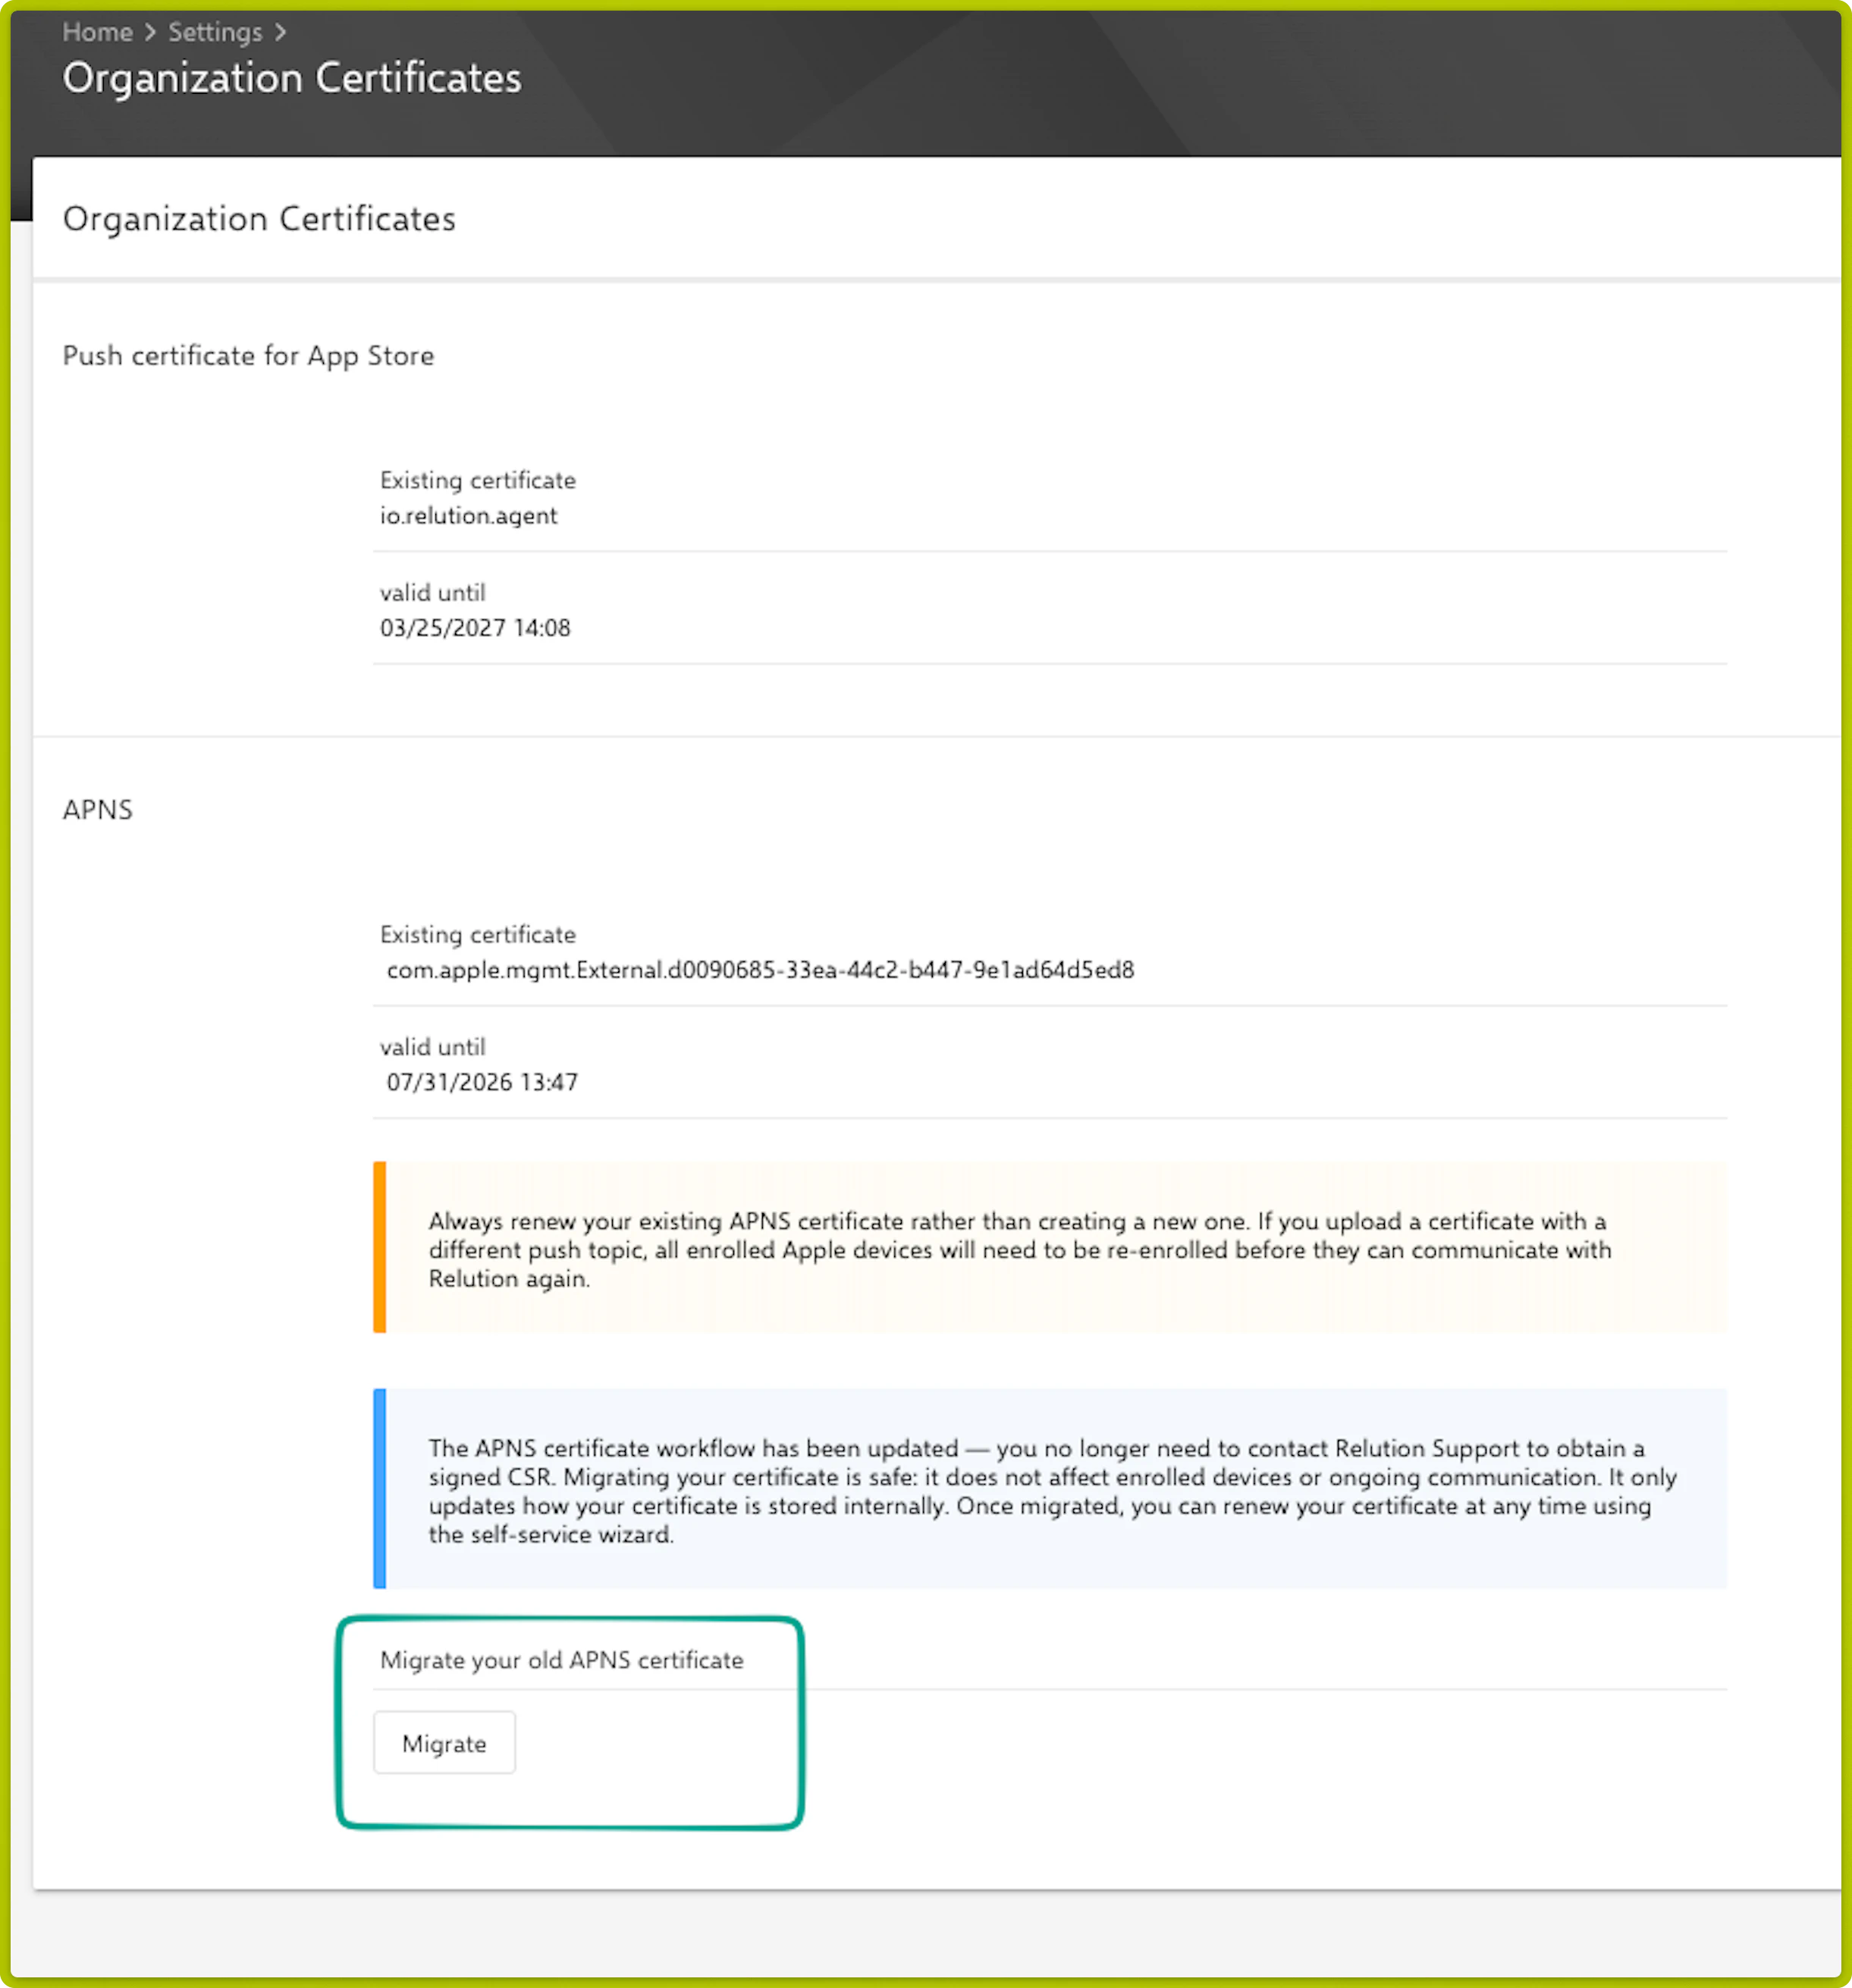
The migration is instantaneous and safe: it has no impact on enrolled devices or ongoing MDM communication. It simply updates how the certificate is stored internally within Relution. After the migration, the Self-Service Wizard can be used for all future certificate renewals.
Setting Up or Renewing a Certificate
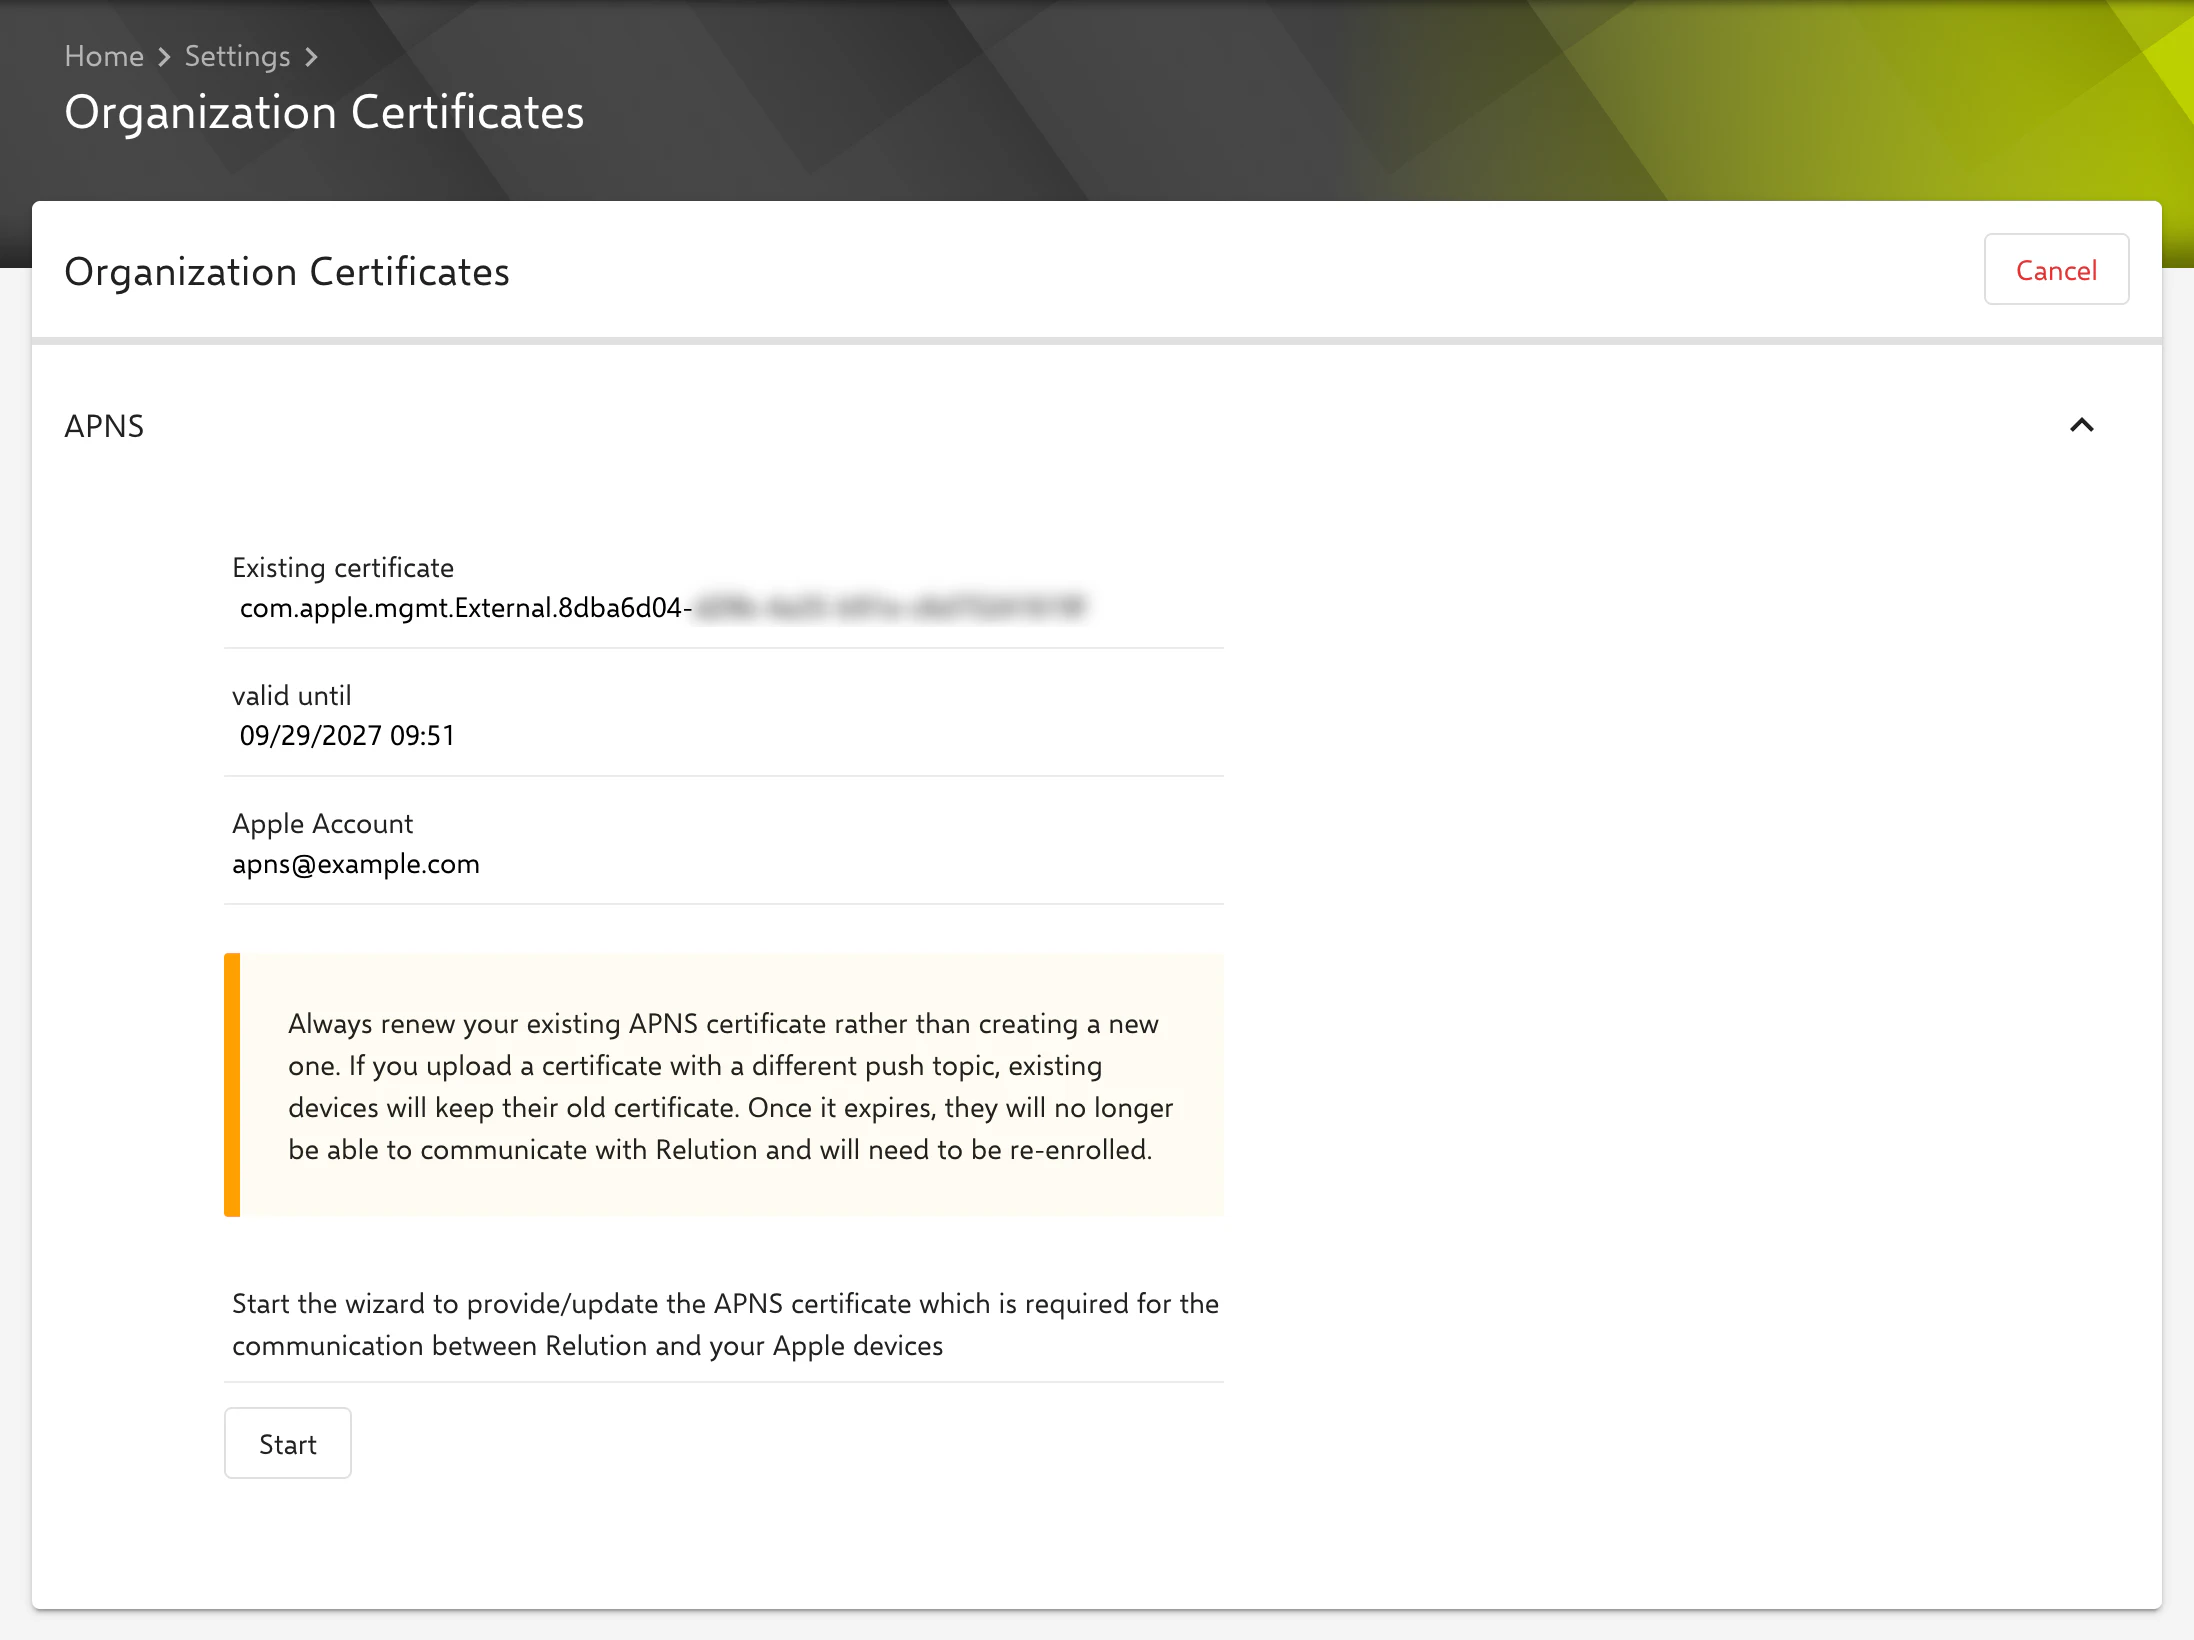
The wizard is opened under Settings → Organization Certificates in the APNS section via the Start button. The section also shows the existing certificate, its expiration date and the stored Apple Account.
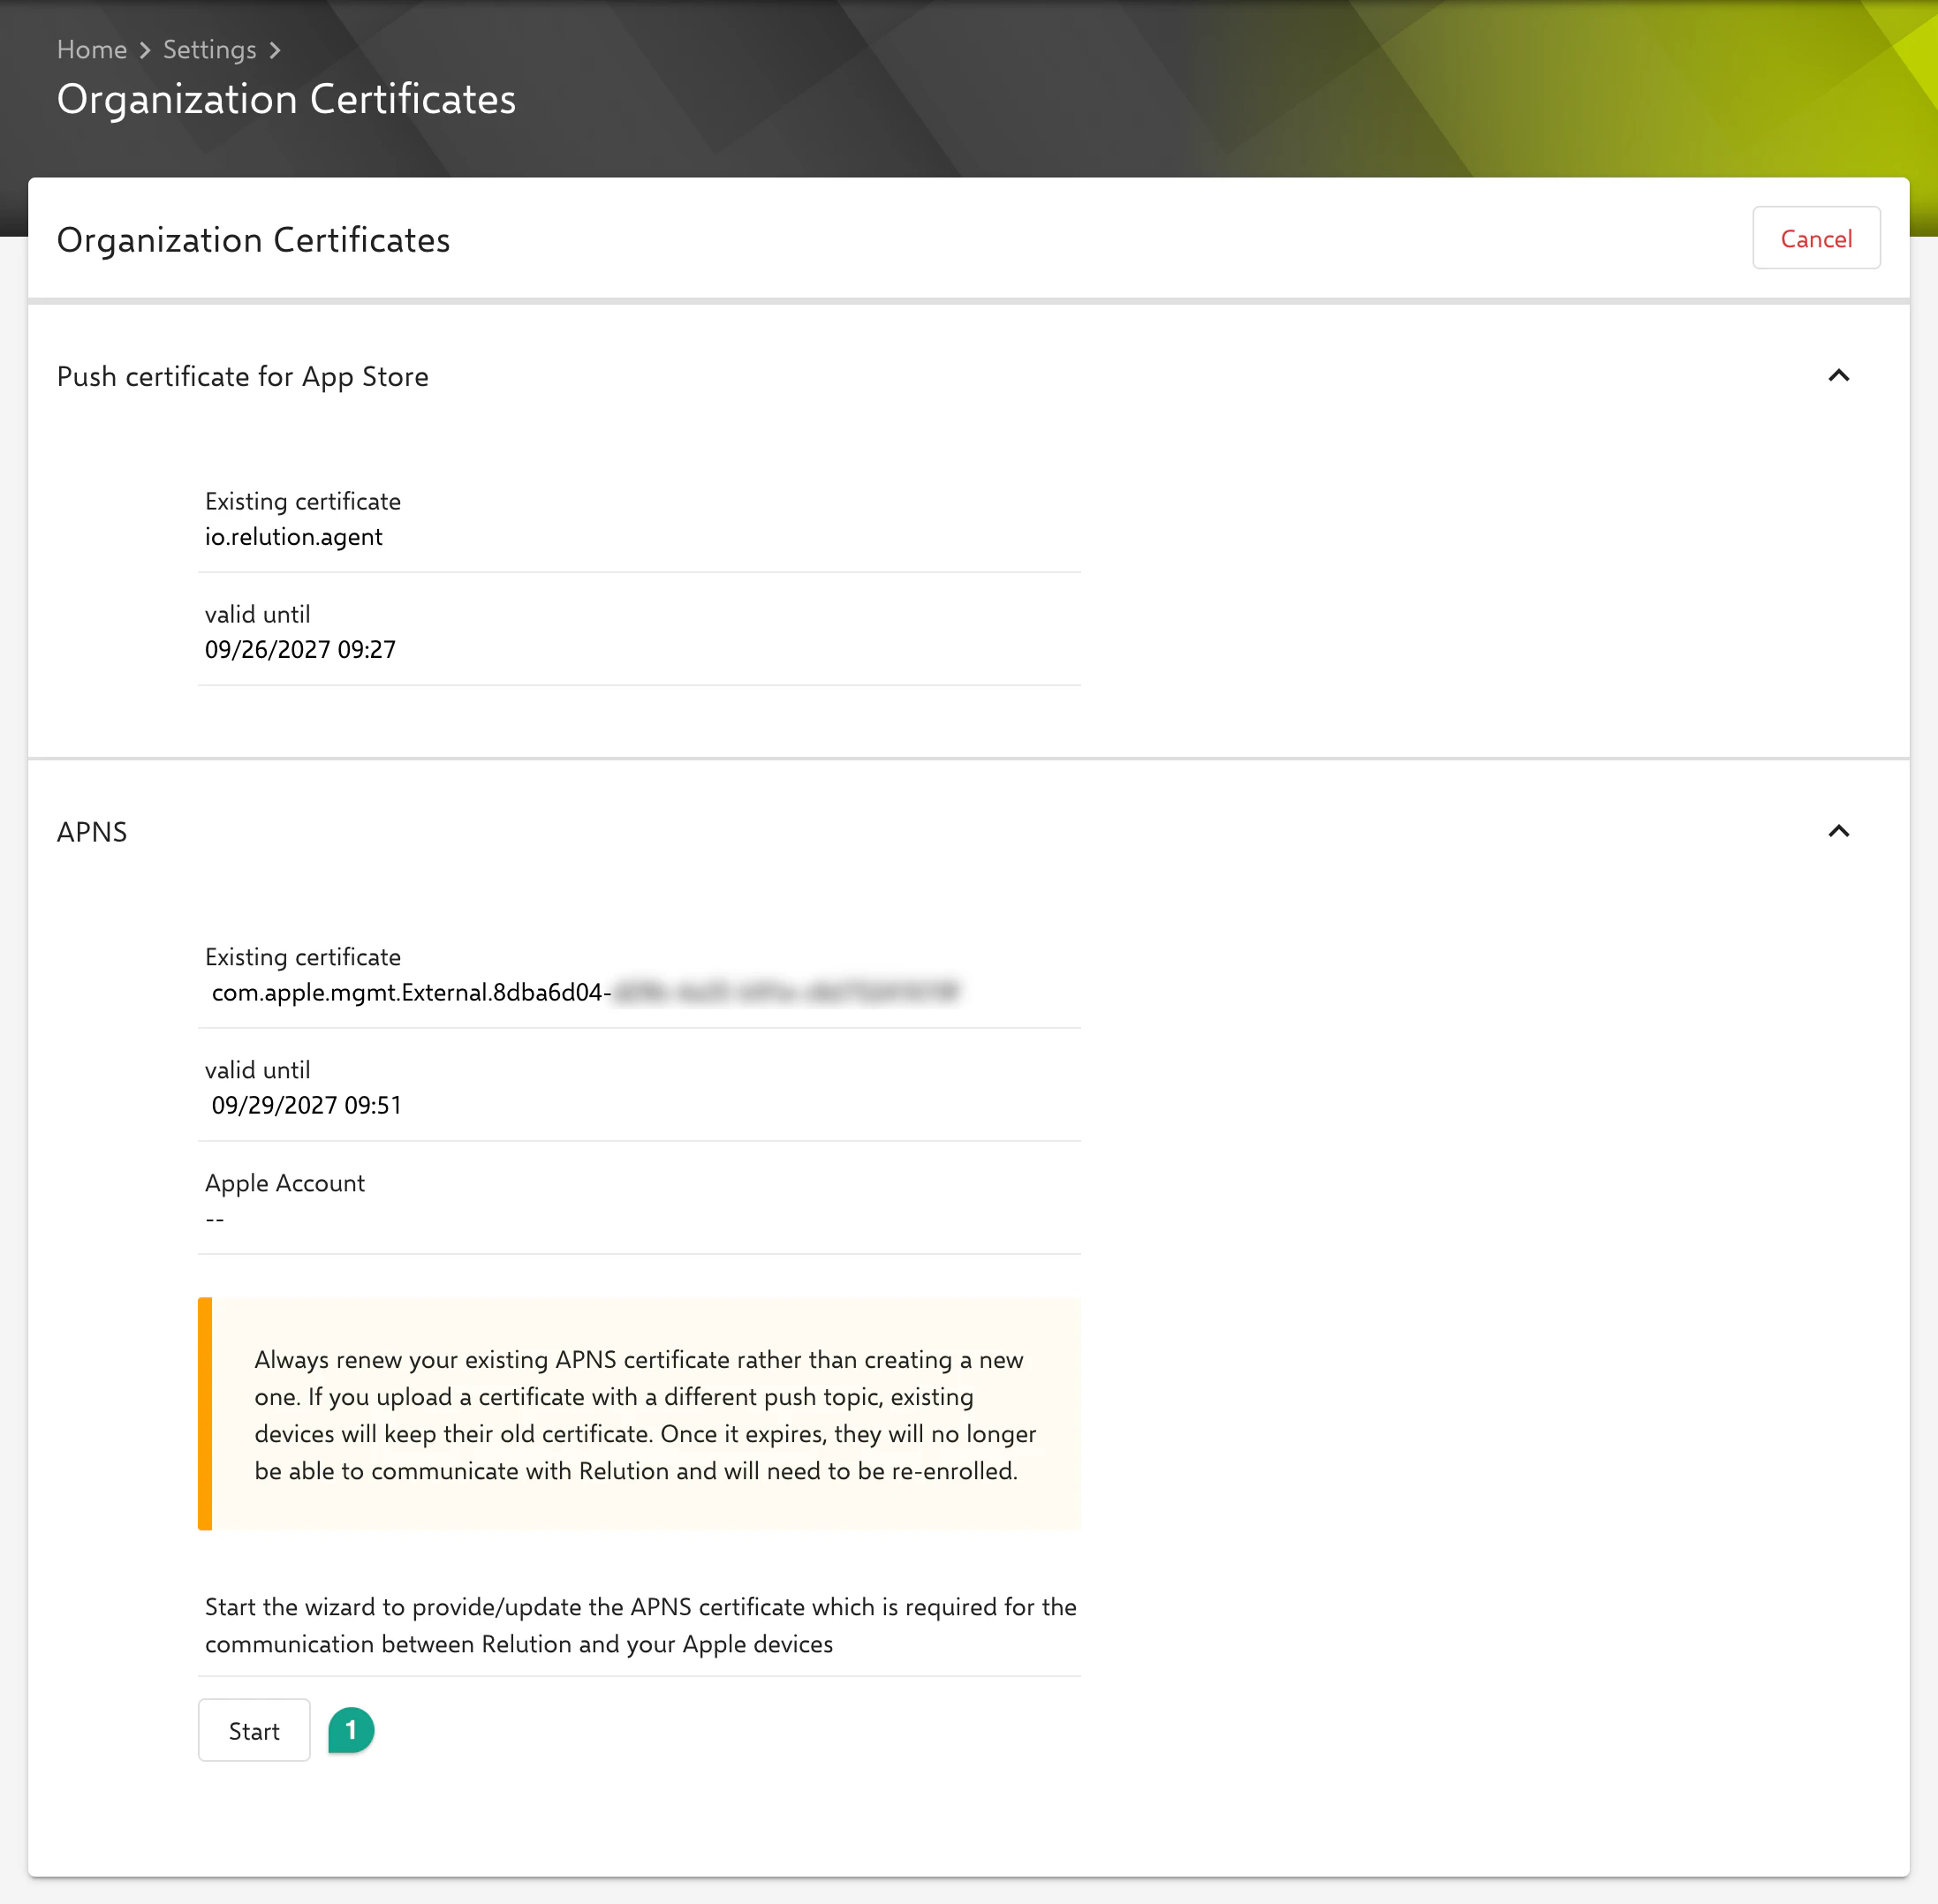
This opens the APNS Certificate Wizard.
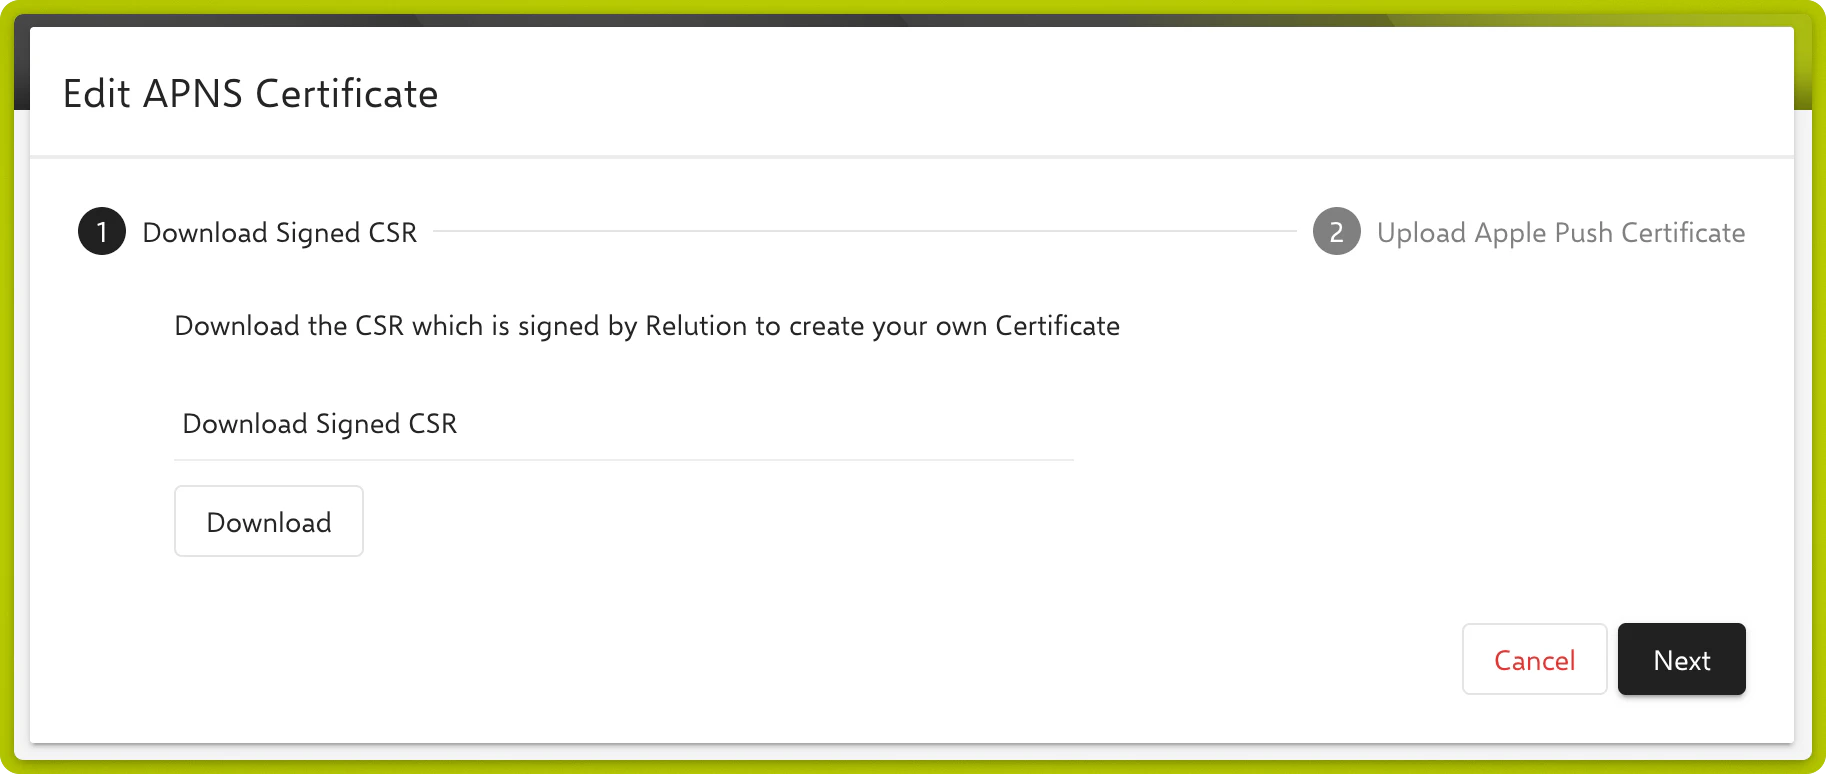
1. Download Signed CSR
Relution automatically generates and signs a Certificate Signing Request (CSR). Download saves it. The wizard is continued with Next only after the download has completed.
2. Upload Apple Push Certificate
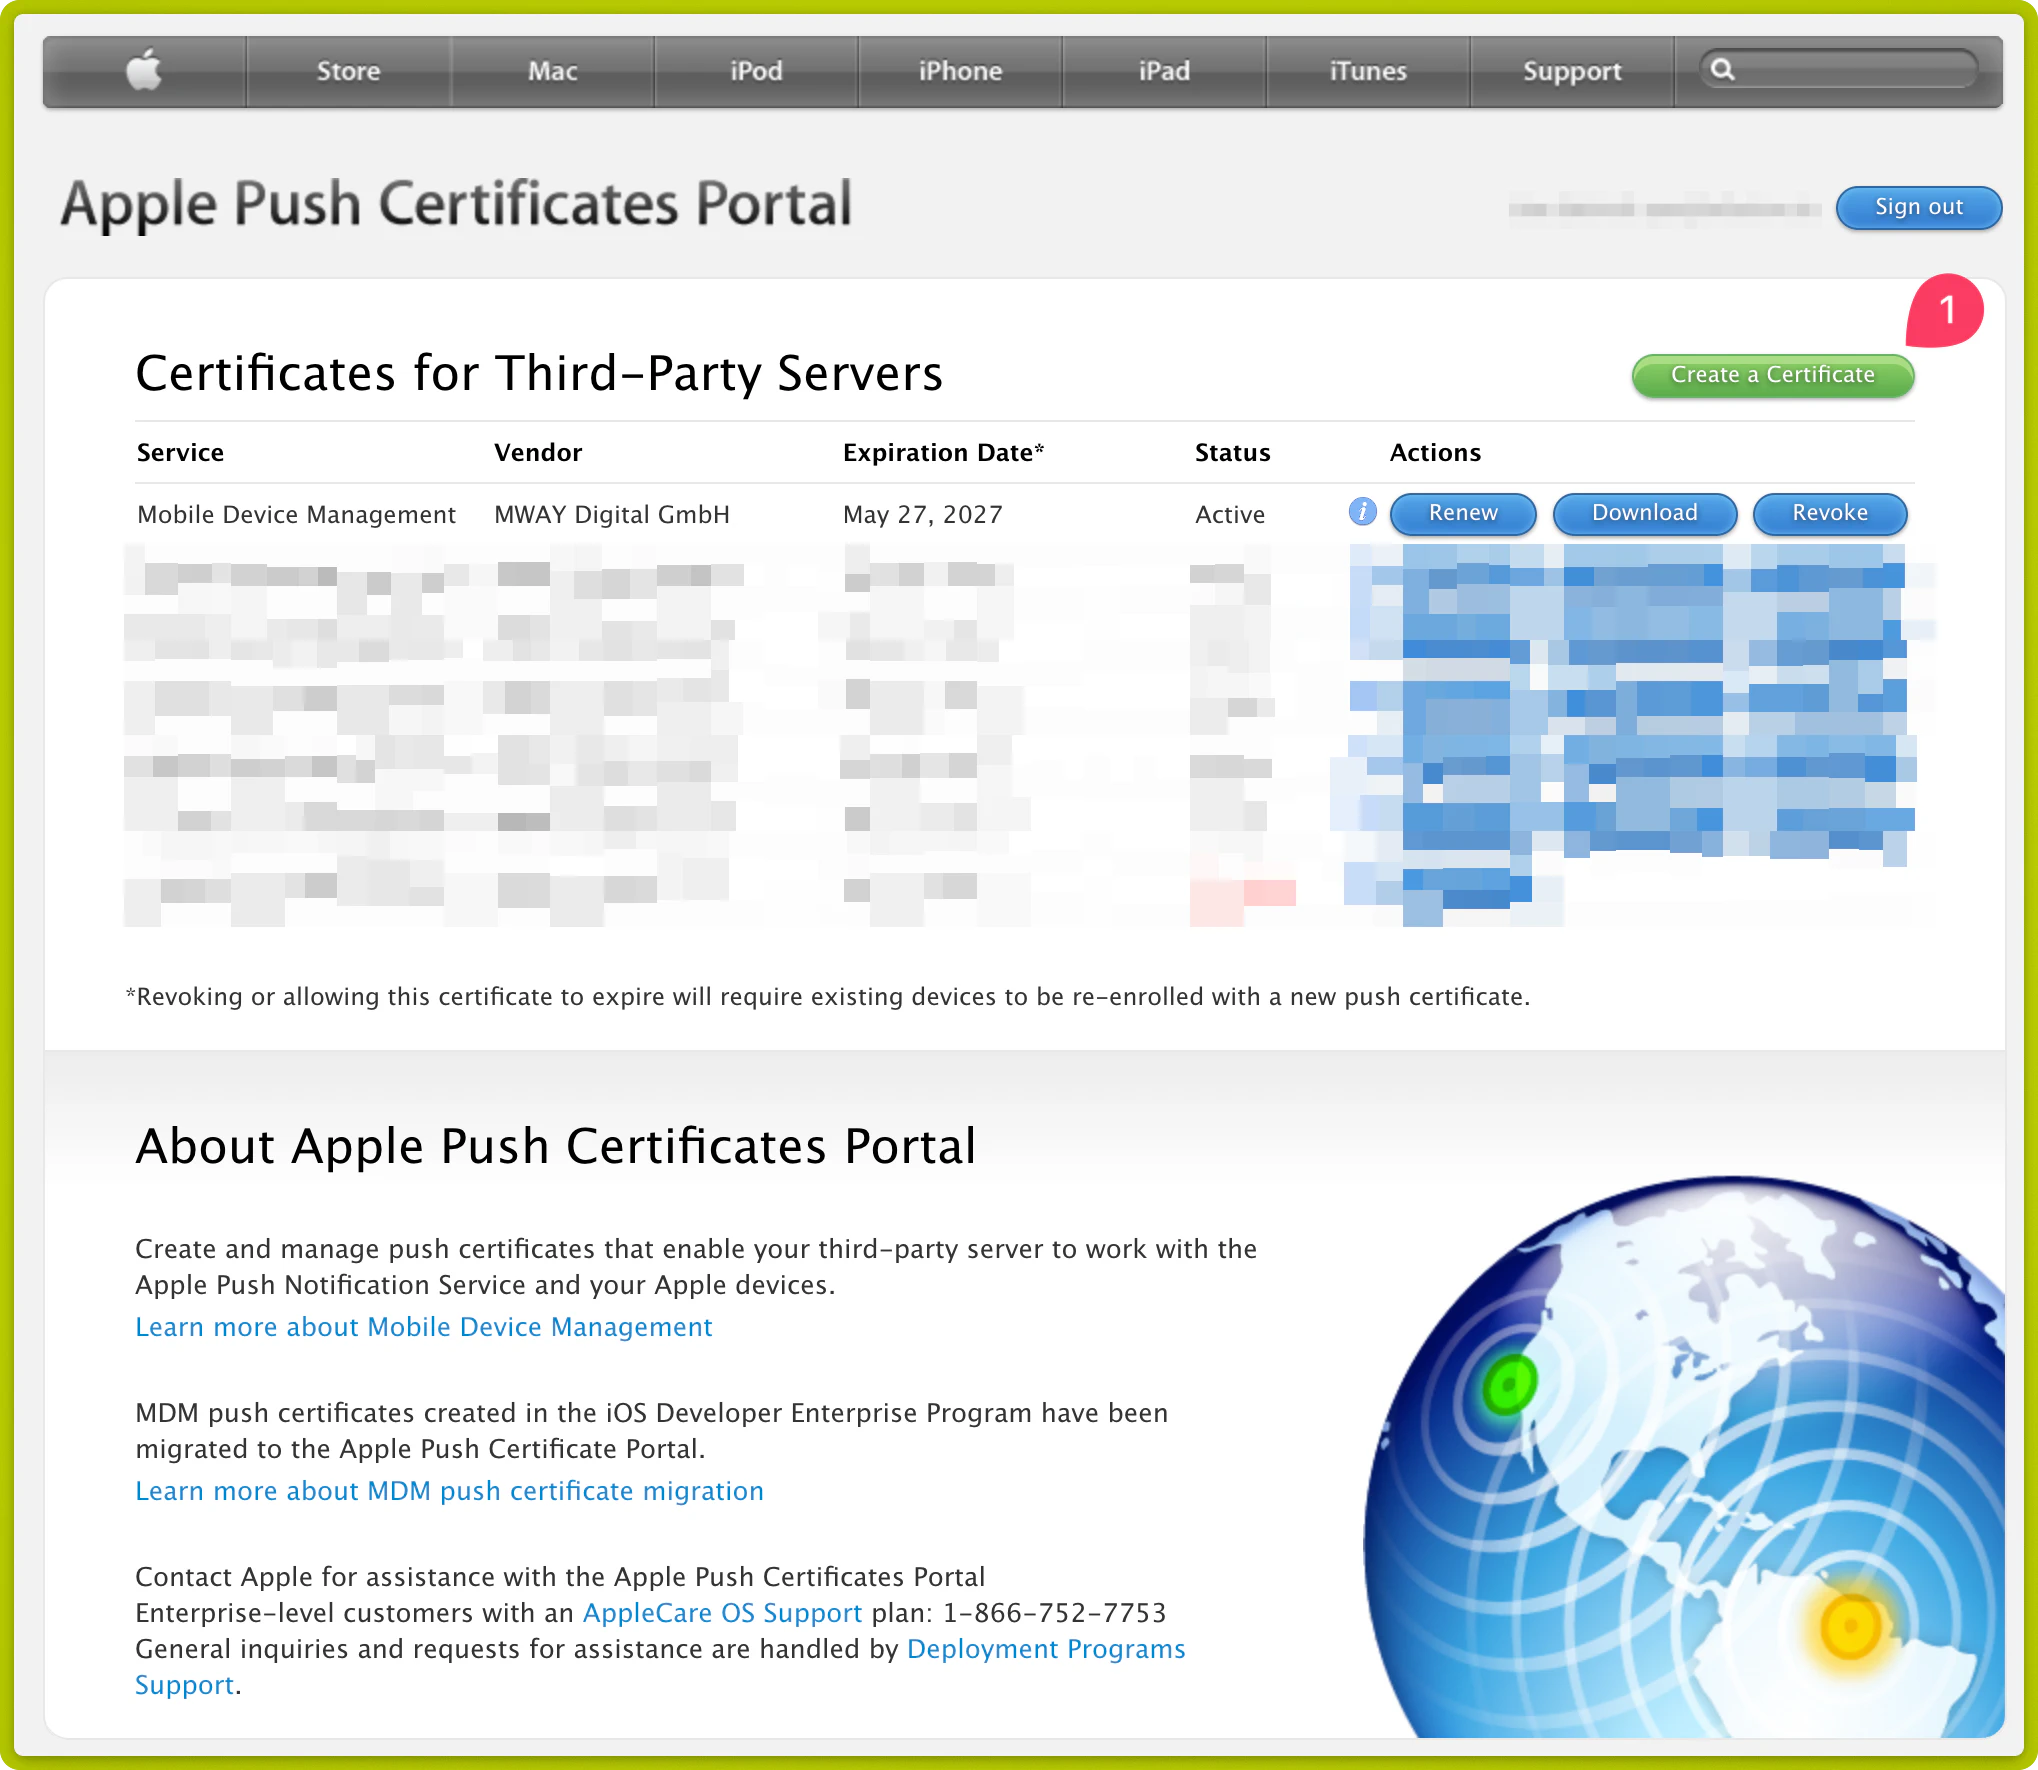
The Apple Push Certificates Portal → is accessed by signing in with the Apple Account.
- Renewing an existing certificate: The certificate is located in the list and renewed via Renew, uploading the CSR file from Step 1. This preserves the push topic, so enrolled devices do not need to be re-enrolled.
- New installation: Create a Certificate creates a new certificate, and the CSR file is uploaded.
The .pem certificate file is then downloaded from the Apple portal.
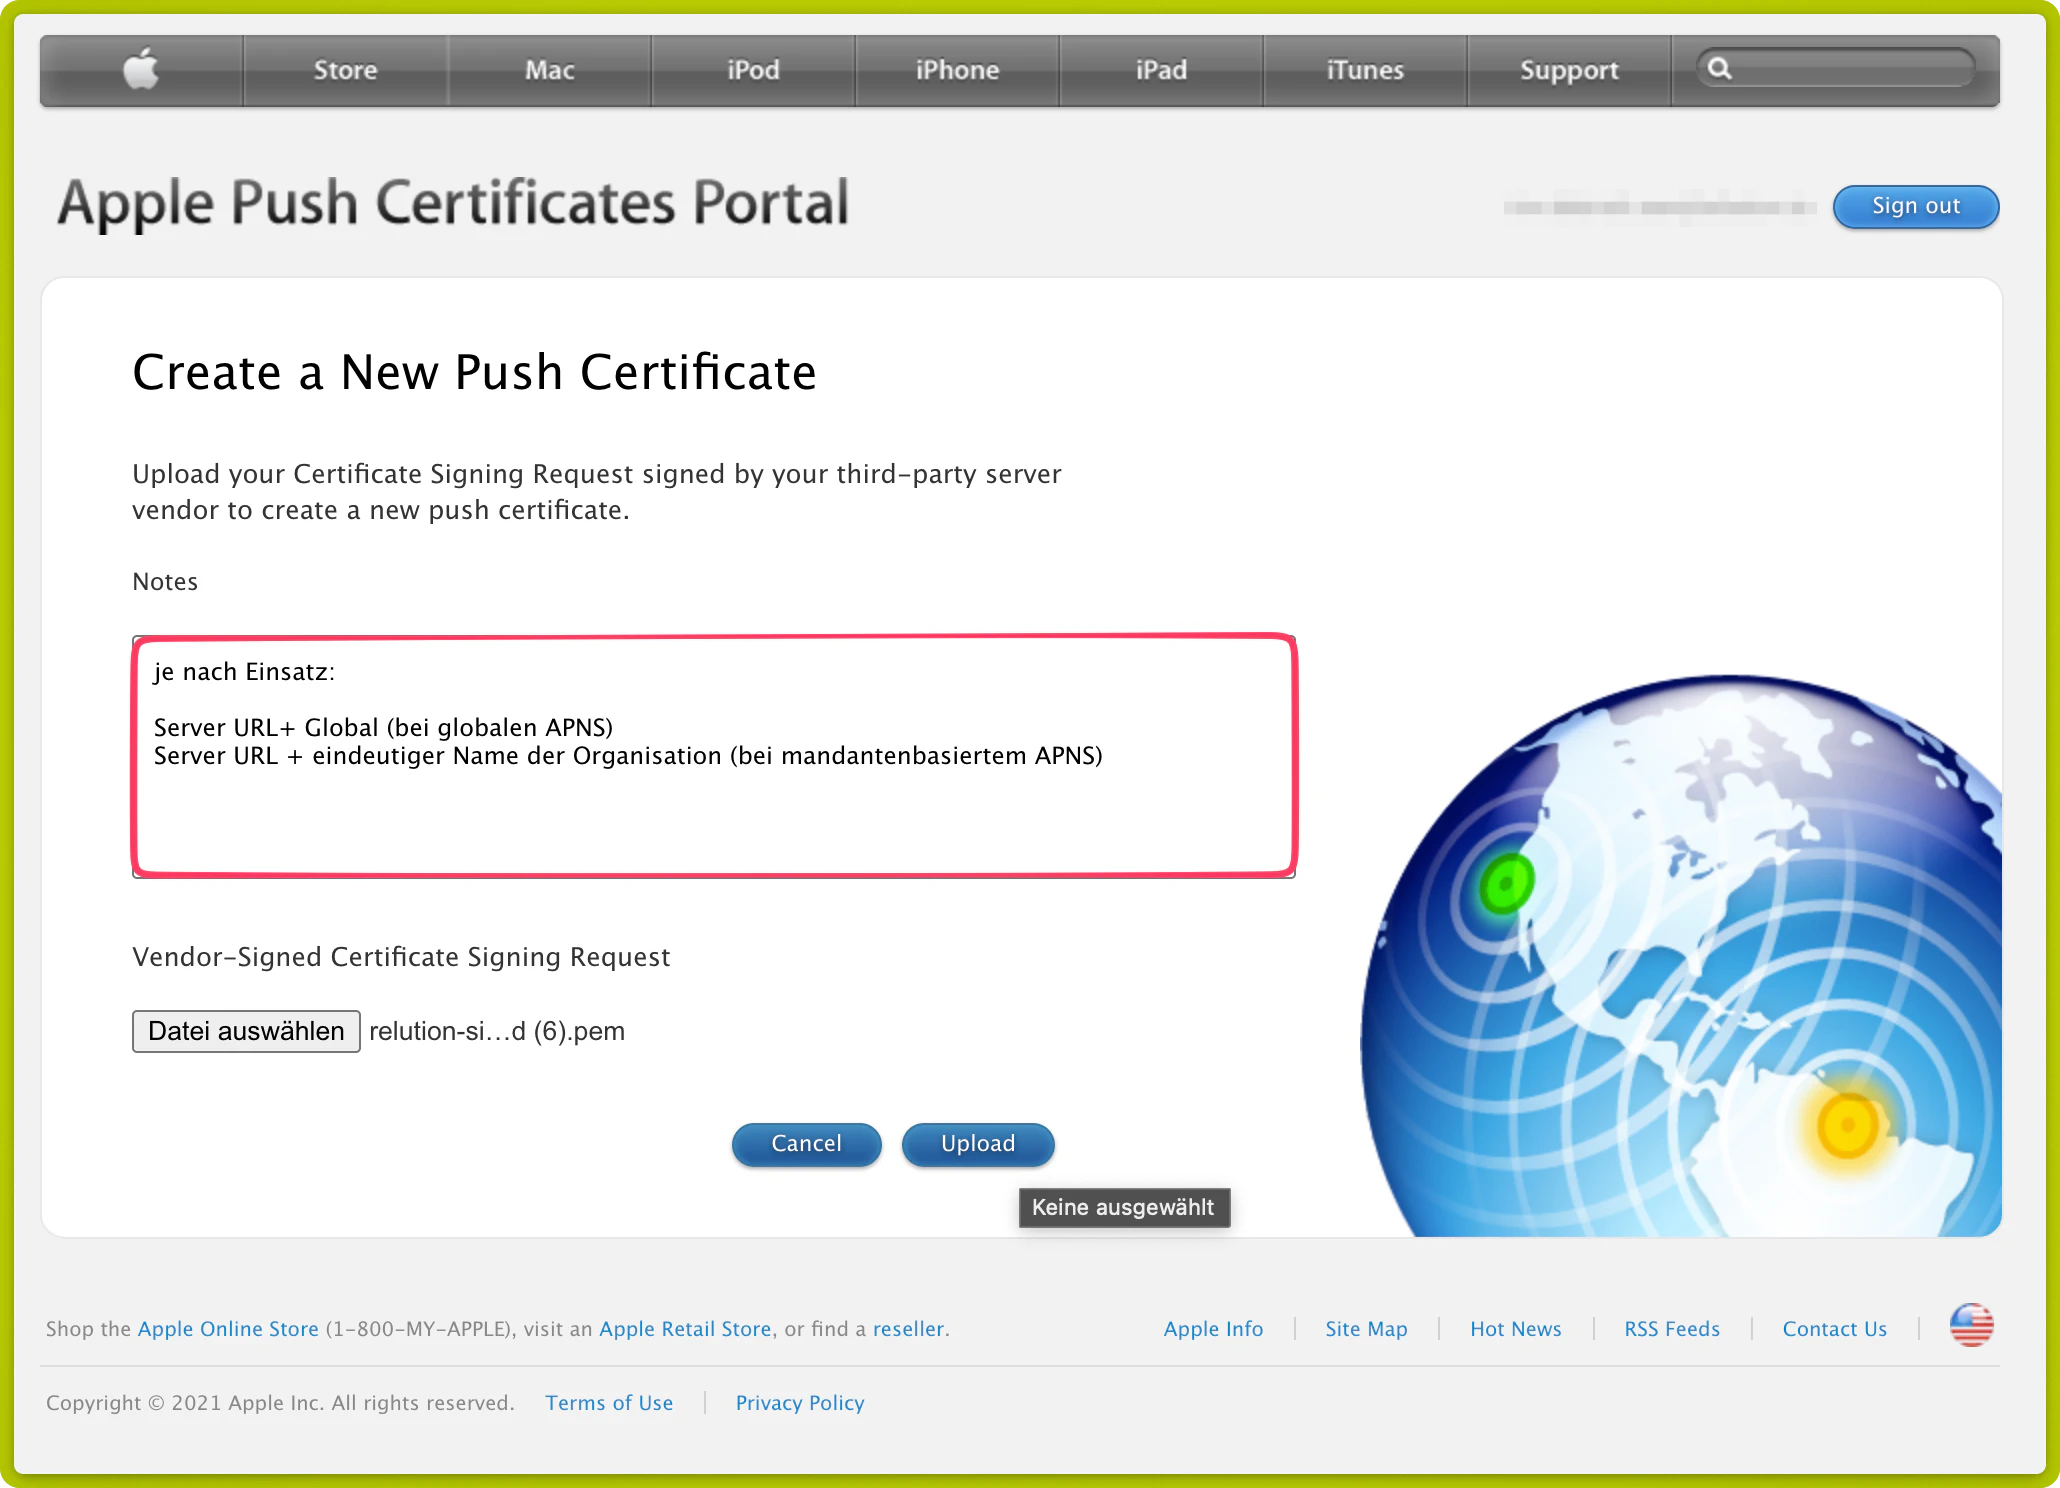
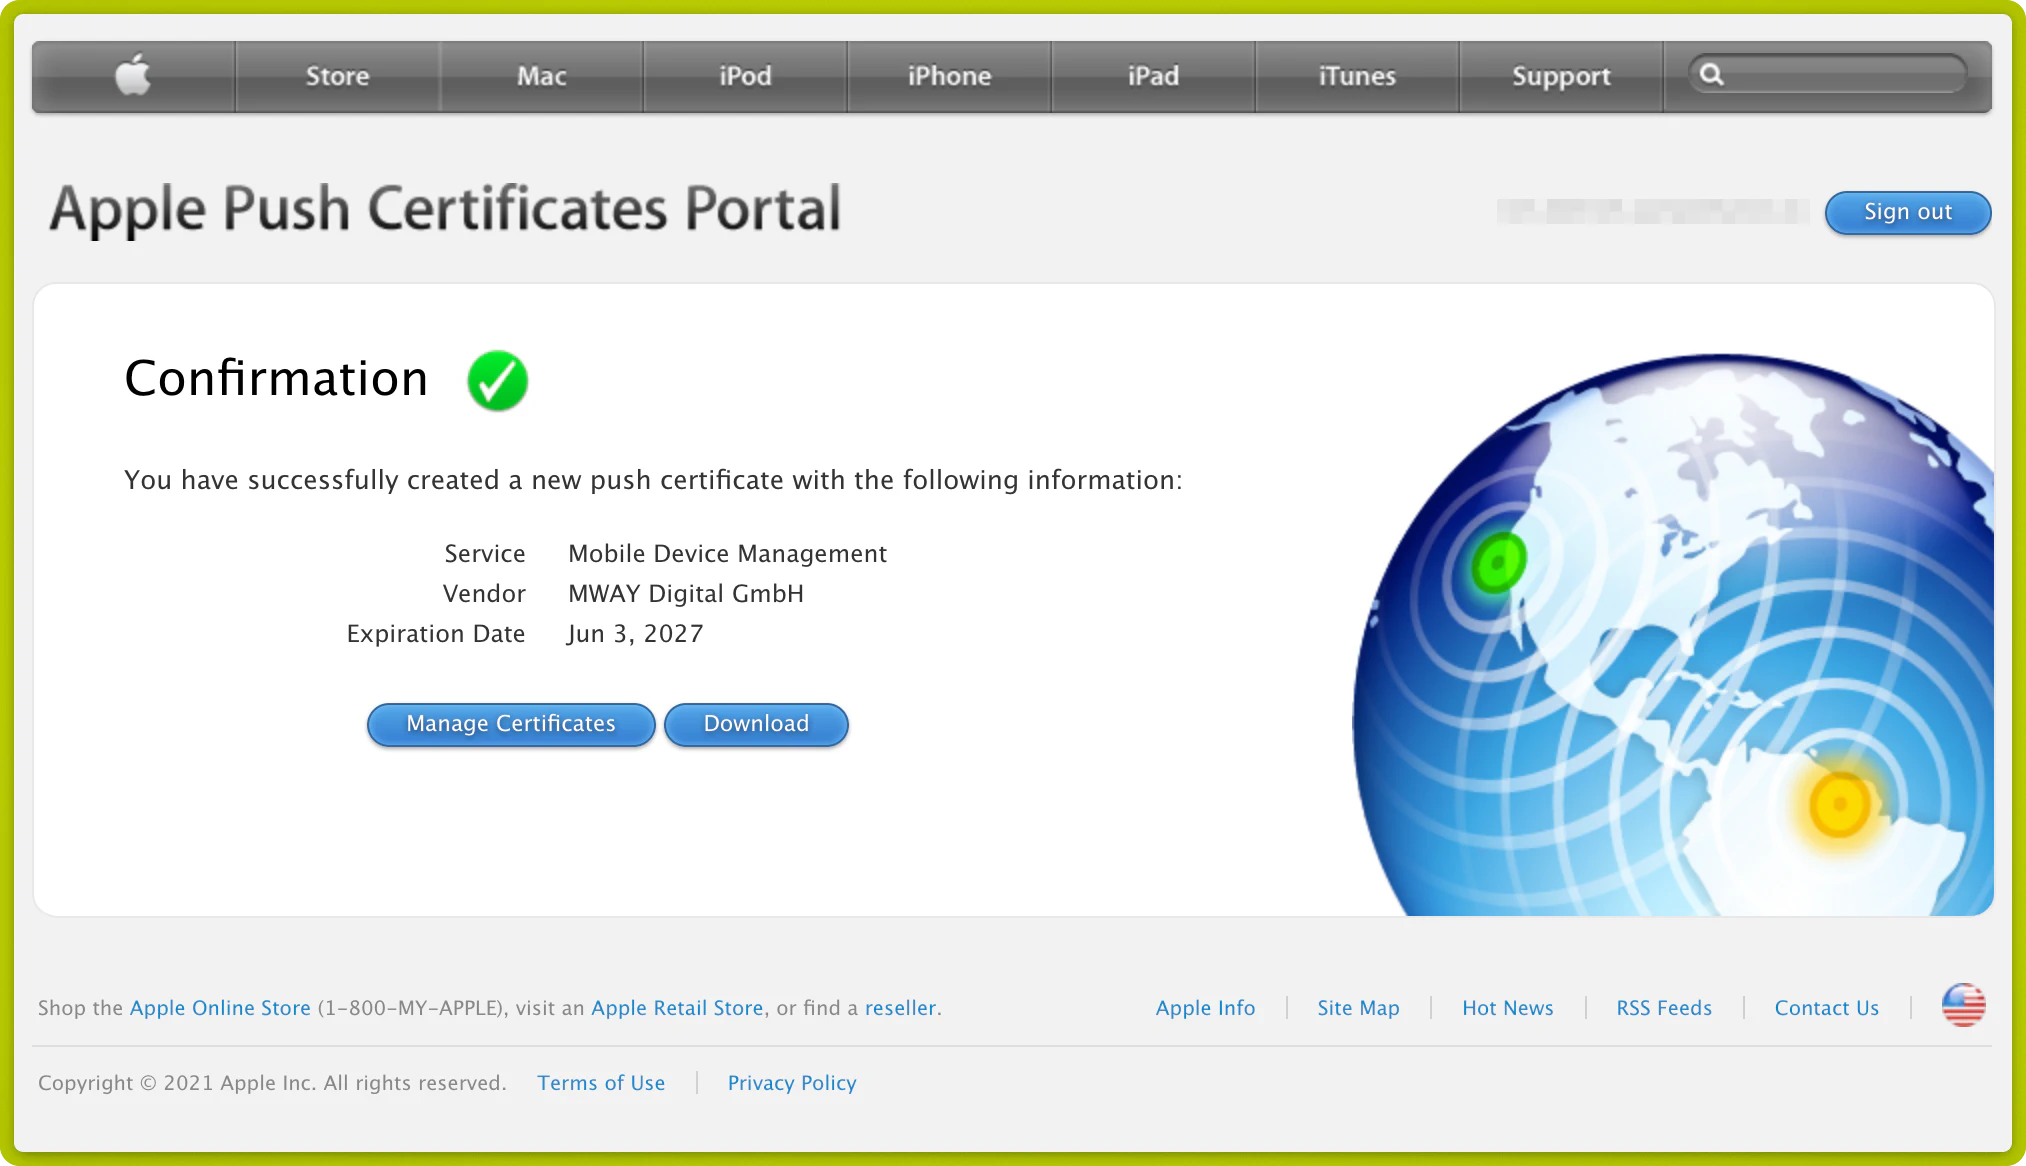
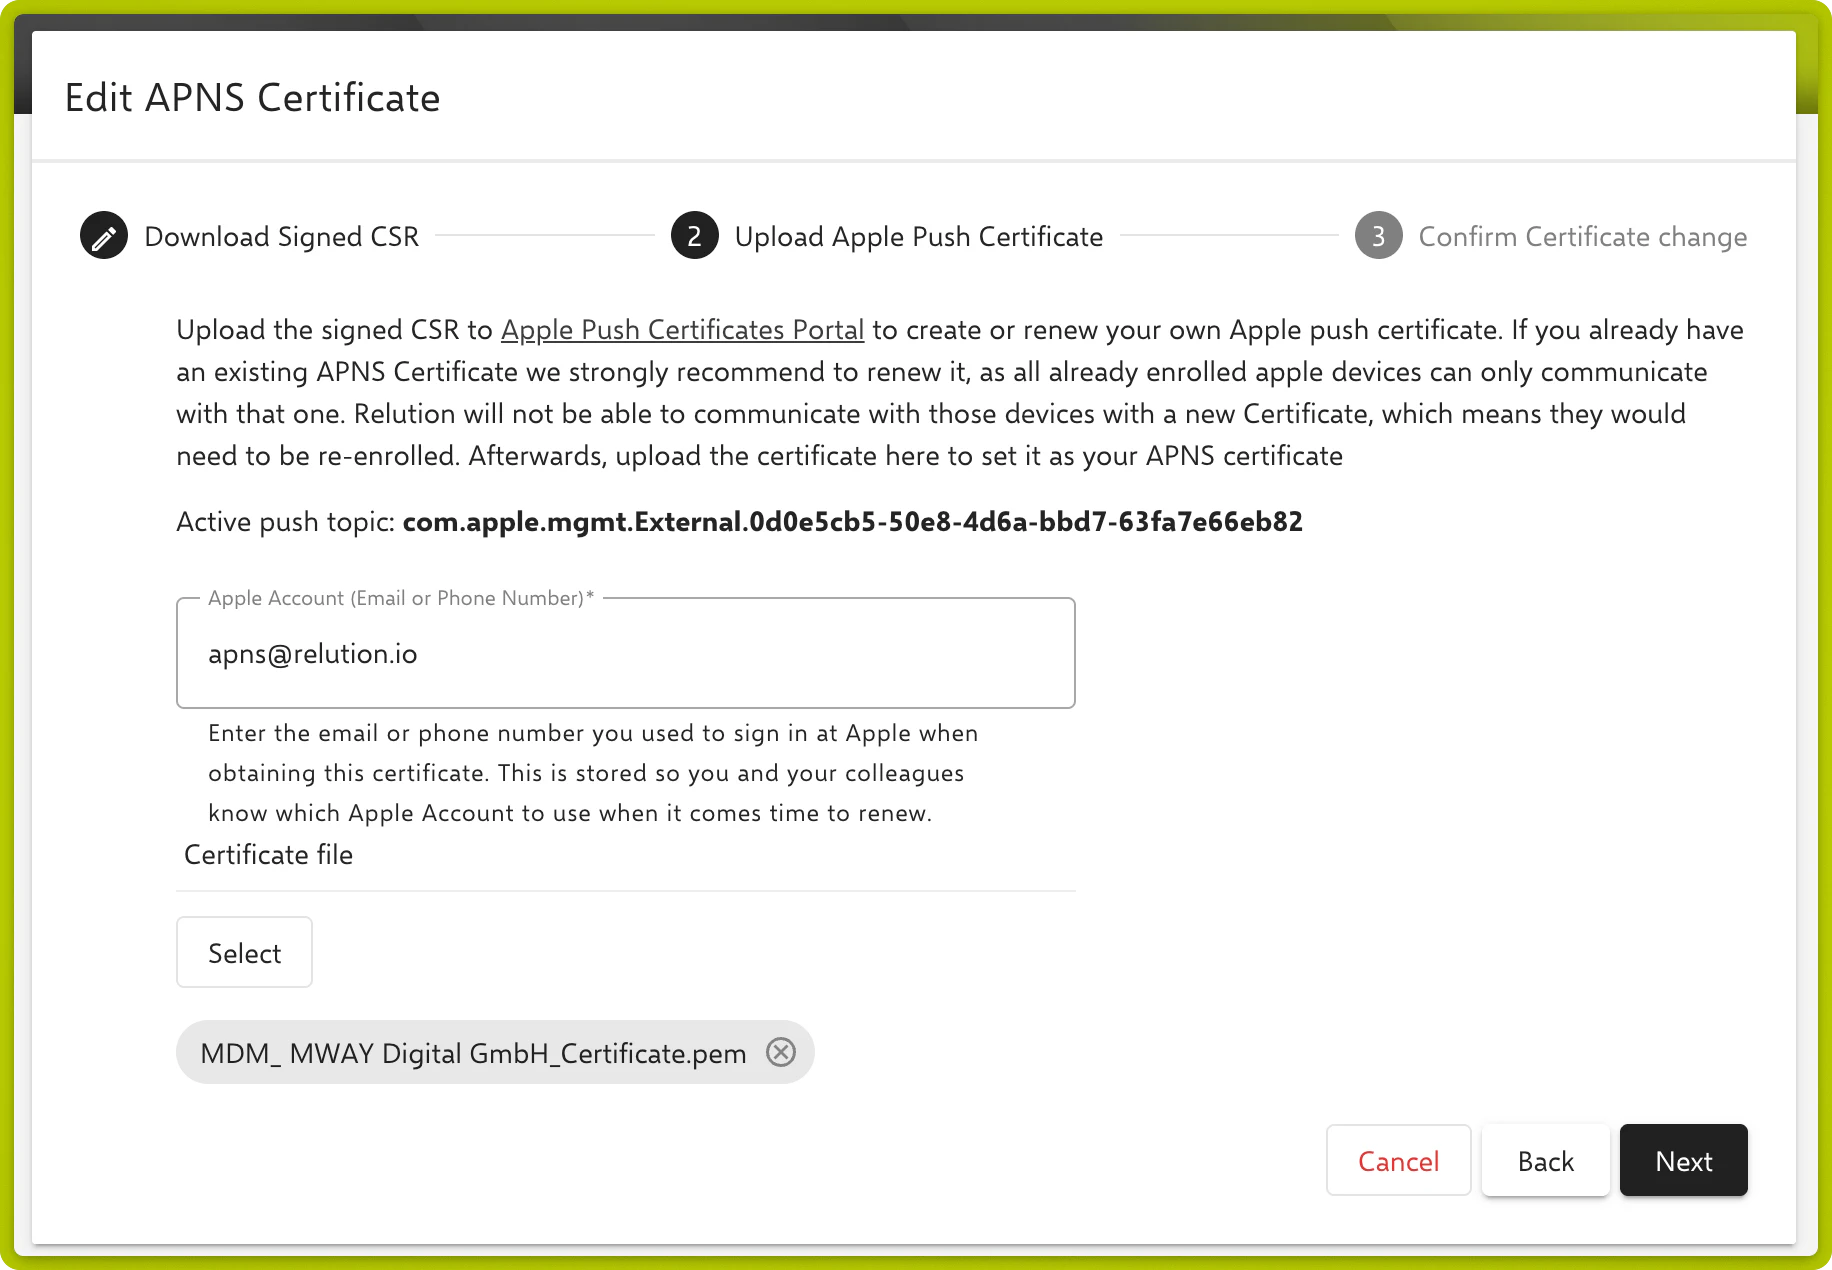
The Apple Account used to create the certificate at Apple is entered in the mandatory field Apple Account (Email or Phone Number). Without an entry, Save remains disabled. The value is stored and pre-fills the field on the next renewal.
The certificate is then uploaded to Relution using the file uploader in this step. Relution rejects expired certificates and the Relution default certificate, and tests the connection to Apple.
Above the file uploader, Active push topic shows the push topic of the certificate currently in effect for the organization (including an inherited one or the Relution default certificate). When renewing, the push topic of the uploaded certificate should match the one displayed.
- If the push topic matches, Save completes the wizard.
- If the push topic has changed, the Next button appears instead of Save and leads to Step 3.
- If no certificate is in effect for the organization yet (shown as No certificate configured), there is nothing to compare: Save completes the wizard and Step 3 is skipped.
3. Confirm Certificate Change (Only in Case of Push Topic Conflict)
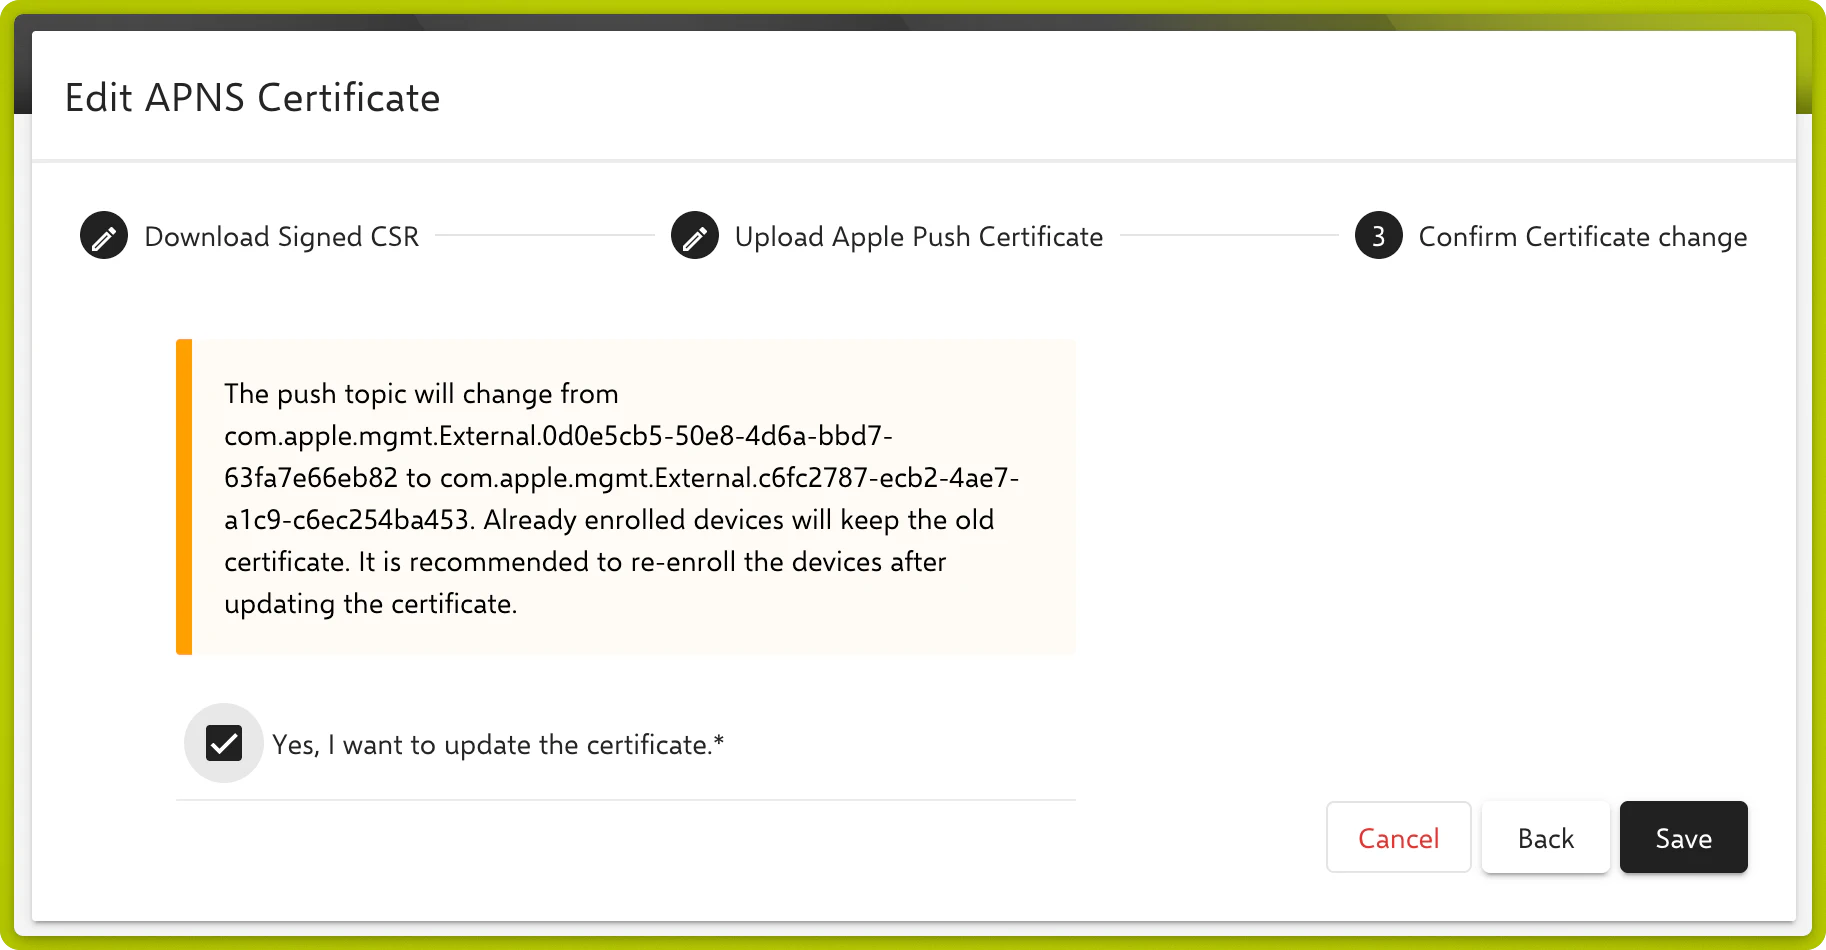
This step only appears if the uploaded certificate has a different push topic than the current one. This can happen if a new certificate was created instead of renewing the existing one, or if a different Apple Account was used.
Changing the push topic affects enrolled Apple devices in the affected organization:
- When transitioning from the Relution-provided certificate to a custom one: Existing devices will keep using the Relution-provided certificate — no immediate re-enrollment is required. Relution plans to retire the shared certificate in the future, but will ensure adequate migration time.
- When replacing the existing certificate with a different one: Enrolled devices will continue using the old certificate until it expires. Once it expires, they will lose MDM communication and must be re-enrolled.
The wizard displays the old and new push topics. To confirm, the Yes, I want to update the certificate checkbox is checked. Save applies the change.
For Apple devices, the APNS Certificate card in the device information shows the UID and expiration date of the certificate used by that device. After a push topic change, this shows which devices still use the old certificate or the Relution default certificate.
Certificate Expiration and Renewal
The Organization Certificates page displays the expiration date of the active certificate. Relution sends an email notification 30 days before expiration and daily from 15 days before expiration. Under Settings → Notifications, the emails APNS certificate will expire soon and APNS certificate has expired can be enabled or disabled individually; both are enabled by default.
The certificate should be renewed before it expires. If the deadline is missed:
- All enrolled Apple devices instantly lose their MDM connection.
- Devices must be re-enrolled after the renewed certificate is uploaded.
Notes
The same Apple Account should always be used when renewing a certificate. Using a different Apple Account creates a new push topic and requires a full re-enrollment of all devices.
The existing certificate should always be renewed instead of creating a new one. Uploading a certificate with a different push topic causes enrolled devices to continue using the old certificate until it expires — after that, they must be re-enrolled.
If a certificate expires, all enrolled Apple devices lose their MDM connection and must be re-enrolled.