 Customer Hub
Login: Access is forbidden
With Relution 26.4.0, the internal application server was switched from Undertow to Tomcat. If the reverse proxy (e.g. nginx or Traefik) runs on a different server than Relution itself, this can result in the following error during login:
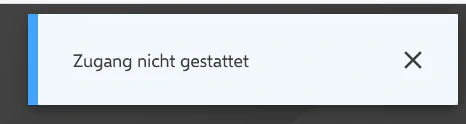
The Relution server log shows a corresponding ERROR entry with the message TLS required.
Cause
For a login to succeed, the connection between the reverse proxy and Relution must satisfy two conditions at the same time:
- The reverse proxy must communicate with Relution from an IP address classified as internal. By default, the private IPv4 ranges
10.0.0.0/8,172.16.0.0/12and192.168.0.0/16, as well as100.64.0.0/10,169.254.0.0/16and127.0.0.0/8(localhost) and the IPv6 rangesfc00::/7,fe80::/10and::1are considered internal. - The
X-Forwarded-Protoheader must be sent by the reverse proxy with the valuehttps.
Only when both conditions are met does Tomcat treat the incoming connection as secured by TLS. If the reverse proxy runs on a separate server with its own (external) IP address, the first condition is already not met. If the X-Forwarded-Proto header is missing or incorrect in addition to or instead of this, the connection is likewise not recognized as secure. In both cases, Relution aborts the login with TLS required in the server log, while the browser shows the message Access is forbidden.
Confirming the cause (optional)
To confirm the cause, DEBUG logging for the relevant Tomcat component can be enabled. To do this, the following entry is added at the top level of the application.yml:
logging:
  level:
    org.apache.catalina.valves.RemoteIpValve: DEBUG
Afterwards, a new login attempt should be made. If an entry like the following then appears in the log, the reverse proxy’s IP address is the cause: the request is not classified as trustworthy.
DEBUG ... ina.valves.RemoteIpValve: Skip RemoteIpValve for request /api/device/v1/currentDevice/actions/next with originalRemoteAddr '<external-IP-of-the-proxy>' []
If this entry does not appear but the error still occurs, the missing or incorrect X-Forwarded-Proto header is the cause instead, see Solution →. If the request is classified as trustworthy, Tomcat logs a line starting with Incoming request. If it contains newSecure=[false], the X-Forwarded-Proto header is missing or does not have the value https.
application.yml (which requires a restart), the log level for org.apache.catalina.valves.RemoteIpValve can also be set to DEBUG at runtime without a restart via the Web API. Via the system portal, this is only possible if it is enabled and the actuator endpoint loggers is exposed. Once the analysis is complete, the log level should be reset to INFO, see Set log level →.Solution
Depending on which of the two conditions from the Cause section is not met, one of the following two adjustments is required — both if necessary.
Trust the reverse proxy’s IP address
For Relution to accept the reverse proxy’s requests, its IP address must be explicitly registered as a trusted internal proxy. To do this, the following entry is added at the top level of the application.yml:
server:
  tomcat:
    remoteip:
      internal-proxies: '<proxy-IP>/32, 10.0.0.0/8, 172.16.0.0/12, 192.168.0.0/16, 169.254.0.0/16, 100.64.0.0/10, 127.0.0.0/8, fc00::/7, fe80::/10, ::1/128'
<proxy-IP> is replaced with the actual IP address of the reverse proxy, e.g. 194.95.62.71/32 (IPv6 with /128). Instead of a single address, a network can also be specified. Additional proxy servers are added separated by commas.
The custom value replaces the default list completely. This is why the default ranges are included in the example; ranges that are not needed can be removed. If the value contains a /, Tomcat reads it as a list of networks in CIDR notation. The older notation as a regular expression (e.g. 194\.95\.62\.71|127\.\d{1,3}\.\d{1,3}\.\d{1,3}) still works but cannot be mixed with the CIDR notation.
The application.yml usually already contains other entries, for example for the system administrator, the external URL, or the database connection. The new server entry is its own top-level key next to the existing relution block, not a sub-item of it — even though a section also named server exists underneath relution (there, e.g., with externalURL). The following example shows the structure with both blocks; existing entries remain unchanged:
server:
  tomcat:
    remoteip:
      internal-proxies: '<proxy-IP>/32, 10.0.0.0/8, 172.16.0.0/12, 192.168.0.0/16, 169.254.0.0/16, 100.64.0.0/10, 127.0.0.0/8, fc00::/7, fe80::/10, ::1/128'

relution:
  # leave existing entries (system, database ...) unchanged
  server:
    externalURL: %EXT_HOSTNAME_URL%
Depending on the type of installation, the file contains further top-level keys. These also remain unchanged.
internal-proxies entry, no additional configuration is required in this case, since private IPv4 ranges are considered internal by default.Set the X-Forwarded-Proto header
In addition, the reverse proxy must forward the X-Forwarded-Proto header with the value https to Relution. The location / block of the nginx configuration must contain the following line for this:
proxy_set_header X-Forwarded-Proto $scheme;
This line is already included in the default relution-nginx.conf template. When using a custom or modified reverse proxy configuration, or if there is an additional proxy in front of it, it should be checked whether the header is set correctly and is not overwritten by an upstream proxy.
After adjusting the application.yml or the reverse proxy configuration, the Relution service or container (and, if applicable, the reverse proxy) must be restarted for the change to take effect.
relution.server.jwt-secure-flag-enabled: false in the application.yml is not a workaround for this error. It only suppresses the TLS required message: the session cookie is then issued without the Secure attribute and is also sent by the browser over unencrypted connections. As of Relution 26.5.7, a warning is written to the server log on every start as long as the entry is set. If it is present, it is removed (default value true) and the cause is fixed instead via server.tomcat.remoteip.internal-proxies and the X-Forwarded-Proto: https header as described above.Additional notes
- This issue primarily affects installations where the reverse proxy does not run on the same host as Relution.
- Relution installations from version 26.4.0 onwards are affected.
- The message
Access is forbiddenis a generic error message that is shown in the portal for a wide variety of requests rejected by the server. The solution described in this article only applies if the server log additionally shows theERRORentryTLS required. - See also: section Nginx Alternative to Traefik (Reverse Proxy) in Docker (Recommended) →