 Customer Hub
Global Organization
In Relution, the Global organization combines the Store organization and the System organization. The store organization is activated automatically.
Identification of the global organization
The new organization has the name Global. Accounts with the authorization of the system administrators and accounts with the authorization of the former Store organization have access to it.
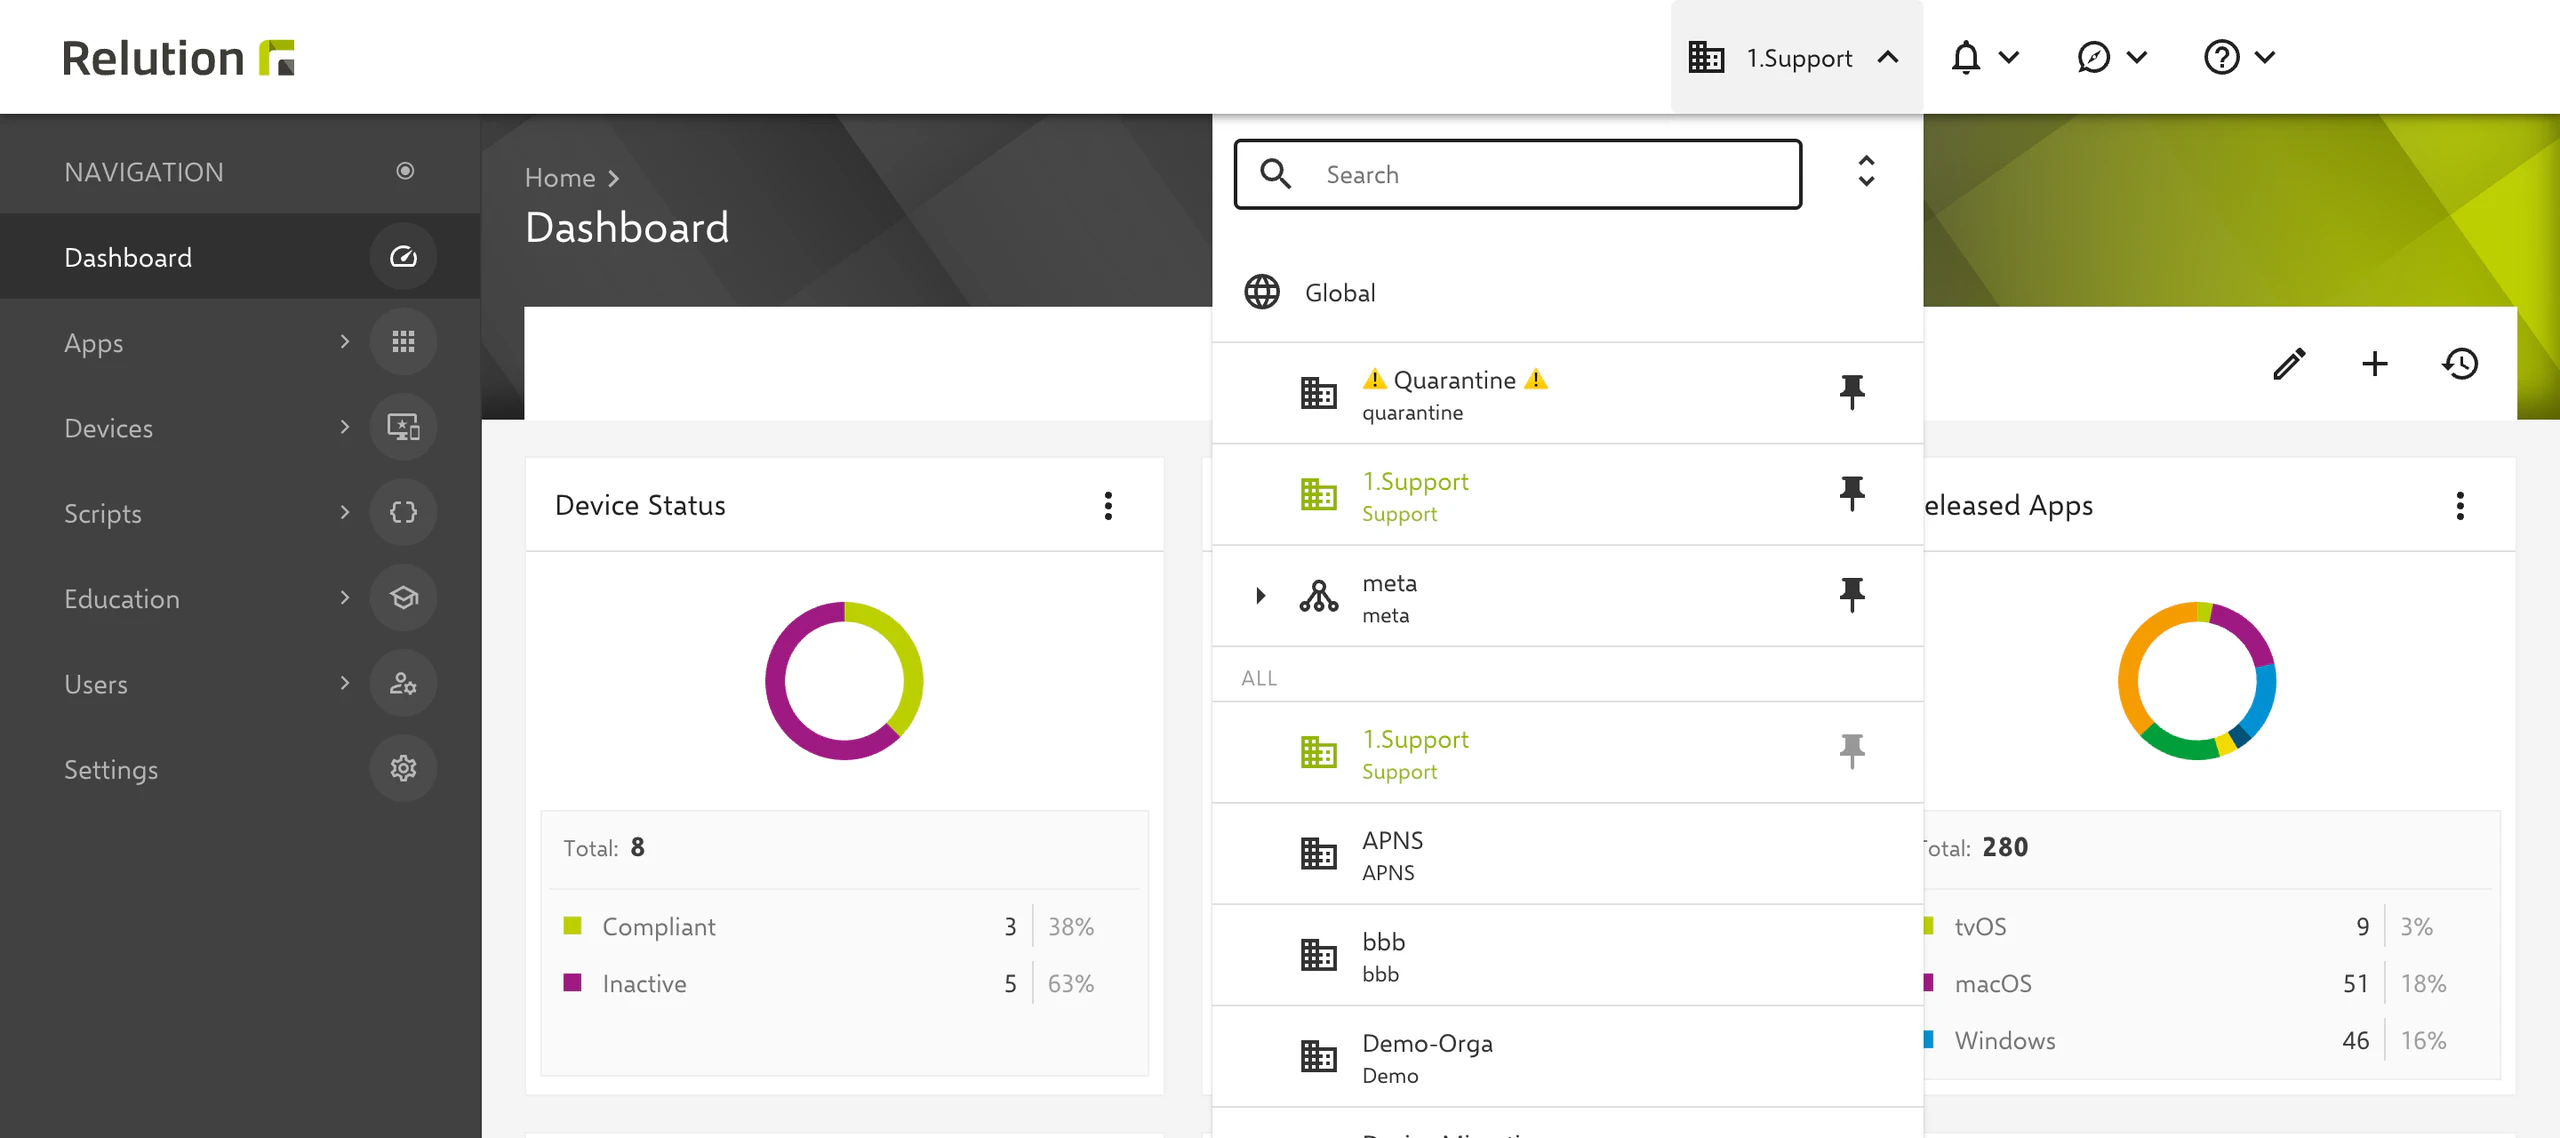
In the organization switcher in the upper right corner, the global organization can be recognized by the globe icon. Meta organizations have a structure icon, sub-organizations have their own icon and standalone organizations have a building icon.
Organization switcher
New in 26.4Clicking the organization name in the top right of the header opens the organization switcher. As of version 26.4, the Global organization is always shown fixed at the top of the list. In addition, individual organizations can be pinned as favorites using the pin icon, so they appear above the full list of organizations for quicker access.
Functionality
The full range of functions is available to users with system administrator authorizations. New organizations can also be created in this organization. This is possible via the newly added menu item Organizations.
Users without authorization for organization administration, i.e. users who have been migrated from an existing store organization, have access to the typical range of functions of the store organization.
Devices cannot be enrolled in the global organization itself. Devices are enrolled and managed in the subordinate organizations.
Apps, policies and scripts can also be provided at the level of a meta organization for its sub-organizations (Meta Organizations →).
Global Users
Users can be created centrally at the global organization level and subsequently assigned to various tenants with specific roles or permissions.
This structure enables flexible identity management: For example, a global user can act as an administrator in Tenant A, while only holding the role of a teacher in Tenant B.
Further information on permissions →
System-wide Automated Device Enrollment
Via Apple School Manager or Apple Business Manager, devices for Automated Device Enrollment (ADE, DEP in the portal) can be assigned to the Global Organization. A DEP profile in the Global Organization with the option Username + Password selected under User authentication assigns the Apple devices to the organization of the signed-in user.
Alternatively, a target organization can be set for an automatic enrollment in the global organization in the Enroll to organization section. The device is then enrolled in this organization, even without user authentication. If Username + Password is also selected, the signed-in user must belong to the target organization. The same approach is possible via meta organizations.
It is still possible to add DEP tokens to other organizations.
Native app distribution and versioning
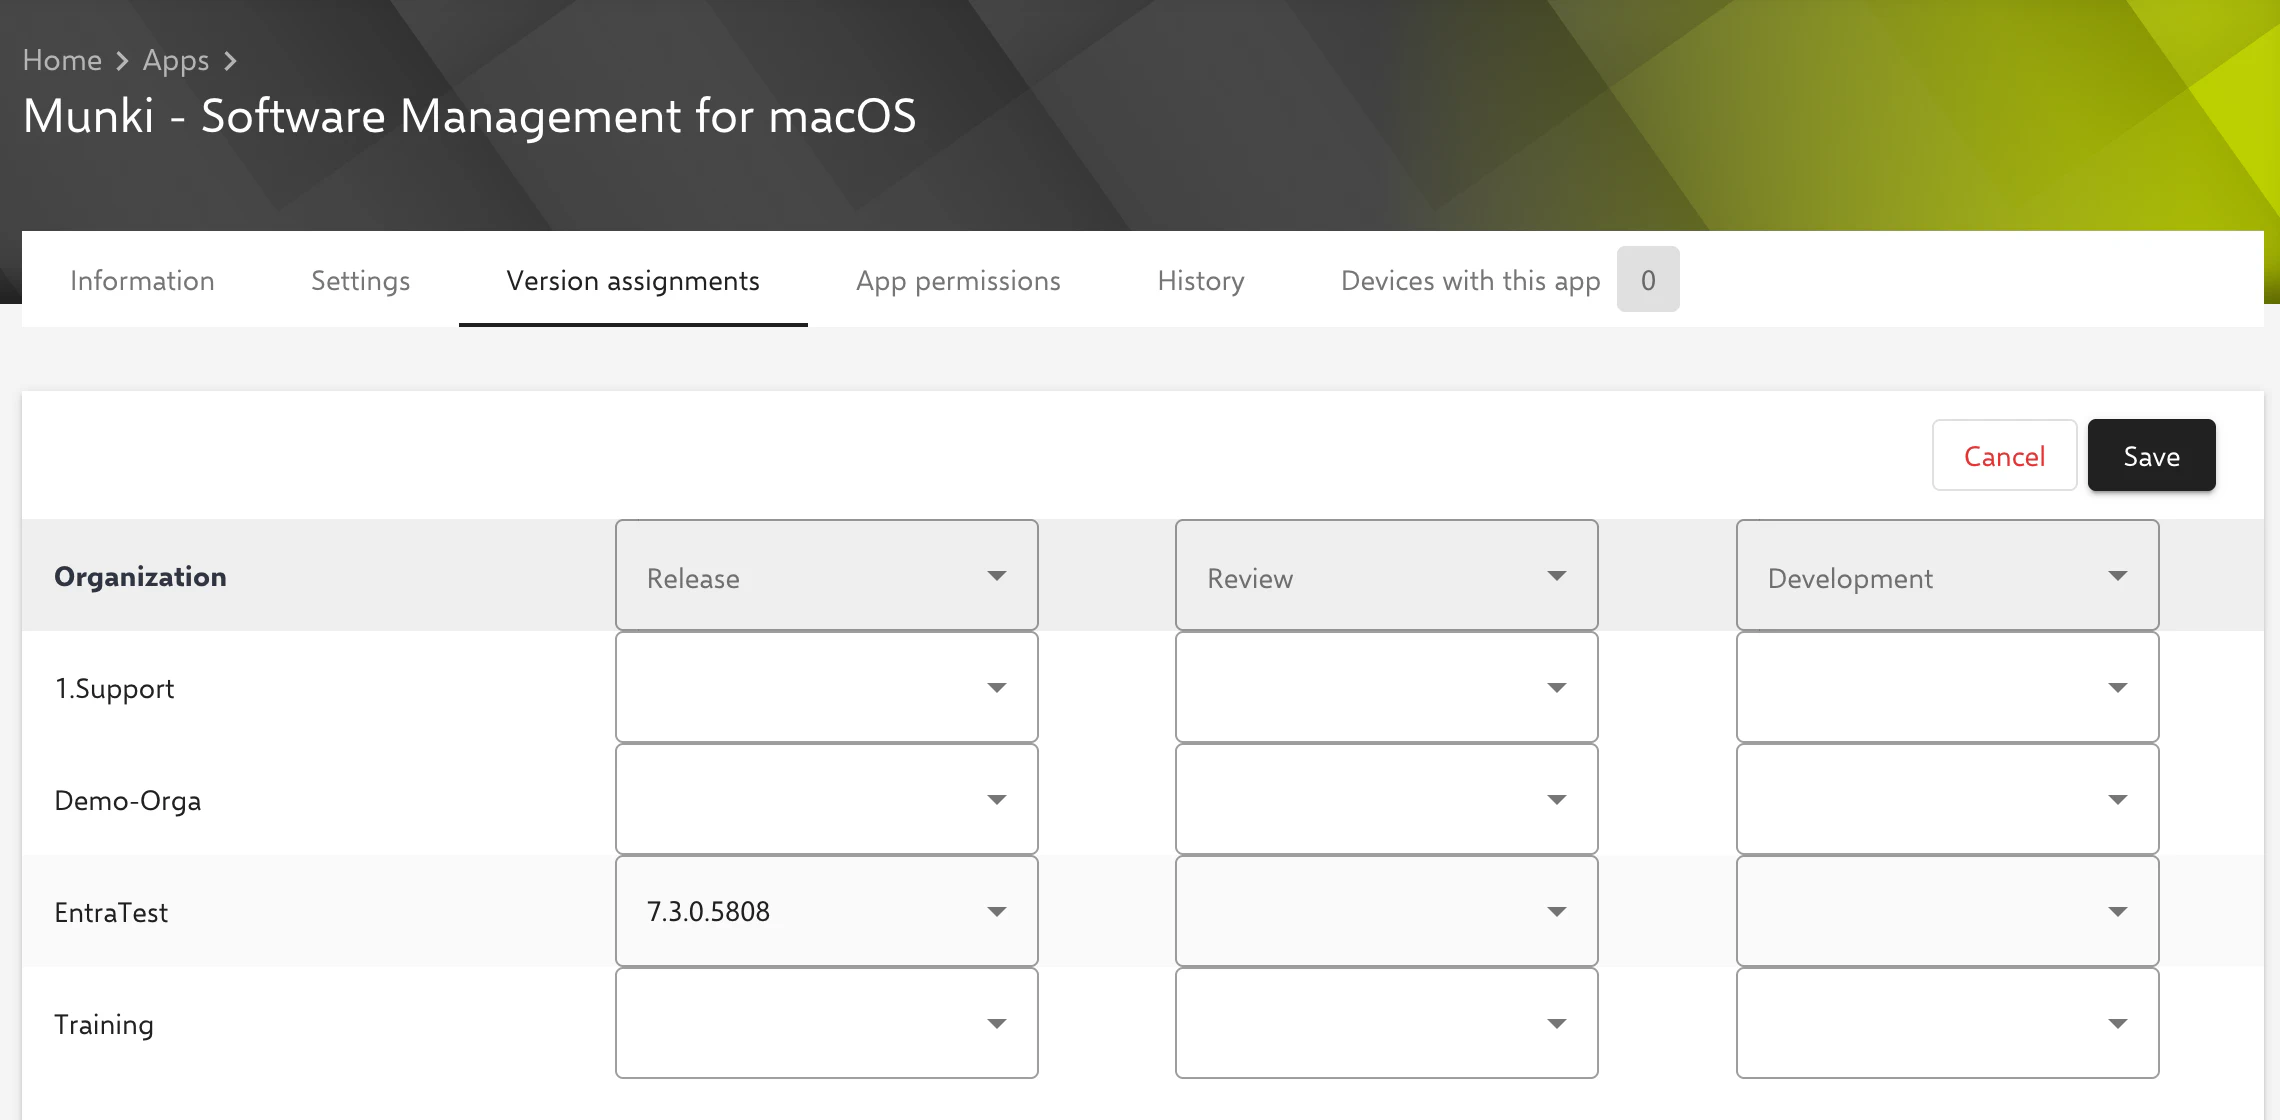
Native apps can be distributed via a policy with the App compliance configuration. The version assignment can be defined in the Global Organization within the app on the Version assignments tab.
Publish policies or copy them to organizations
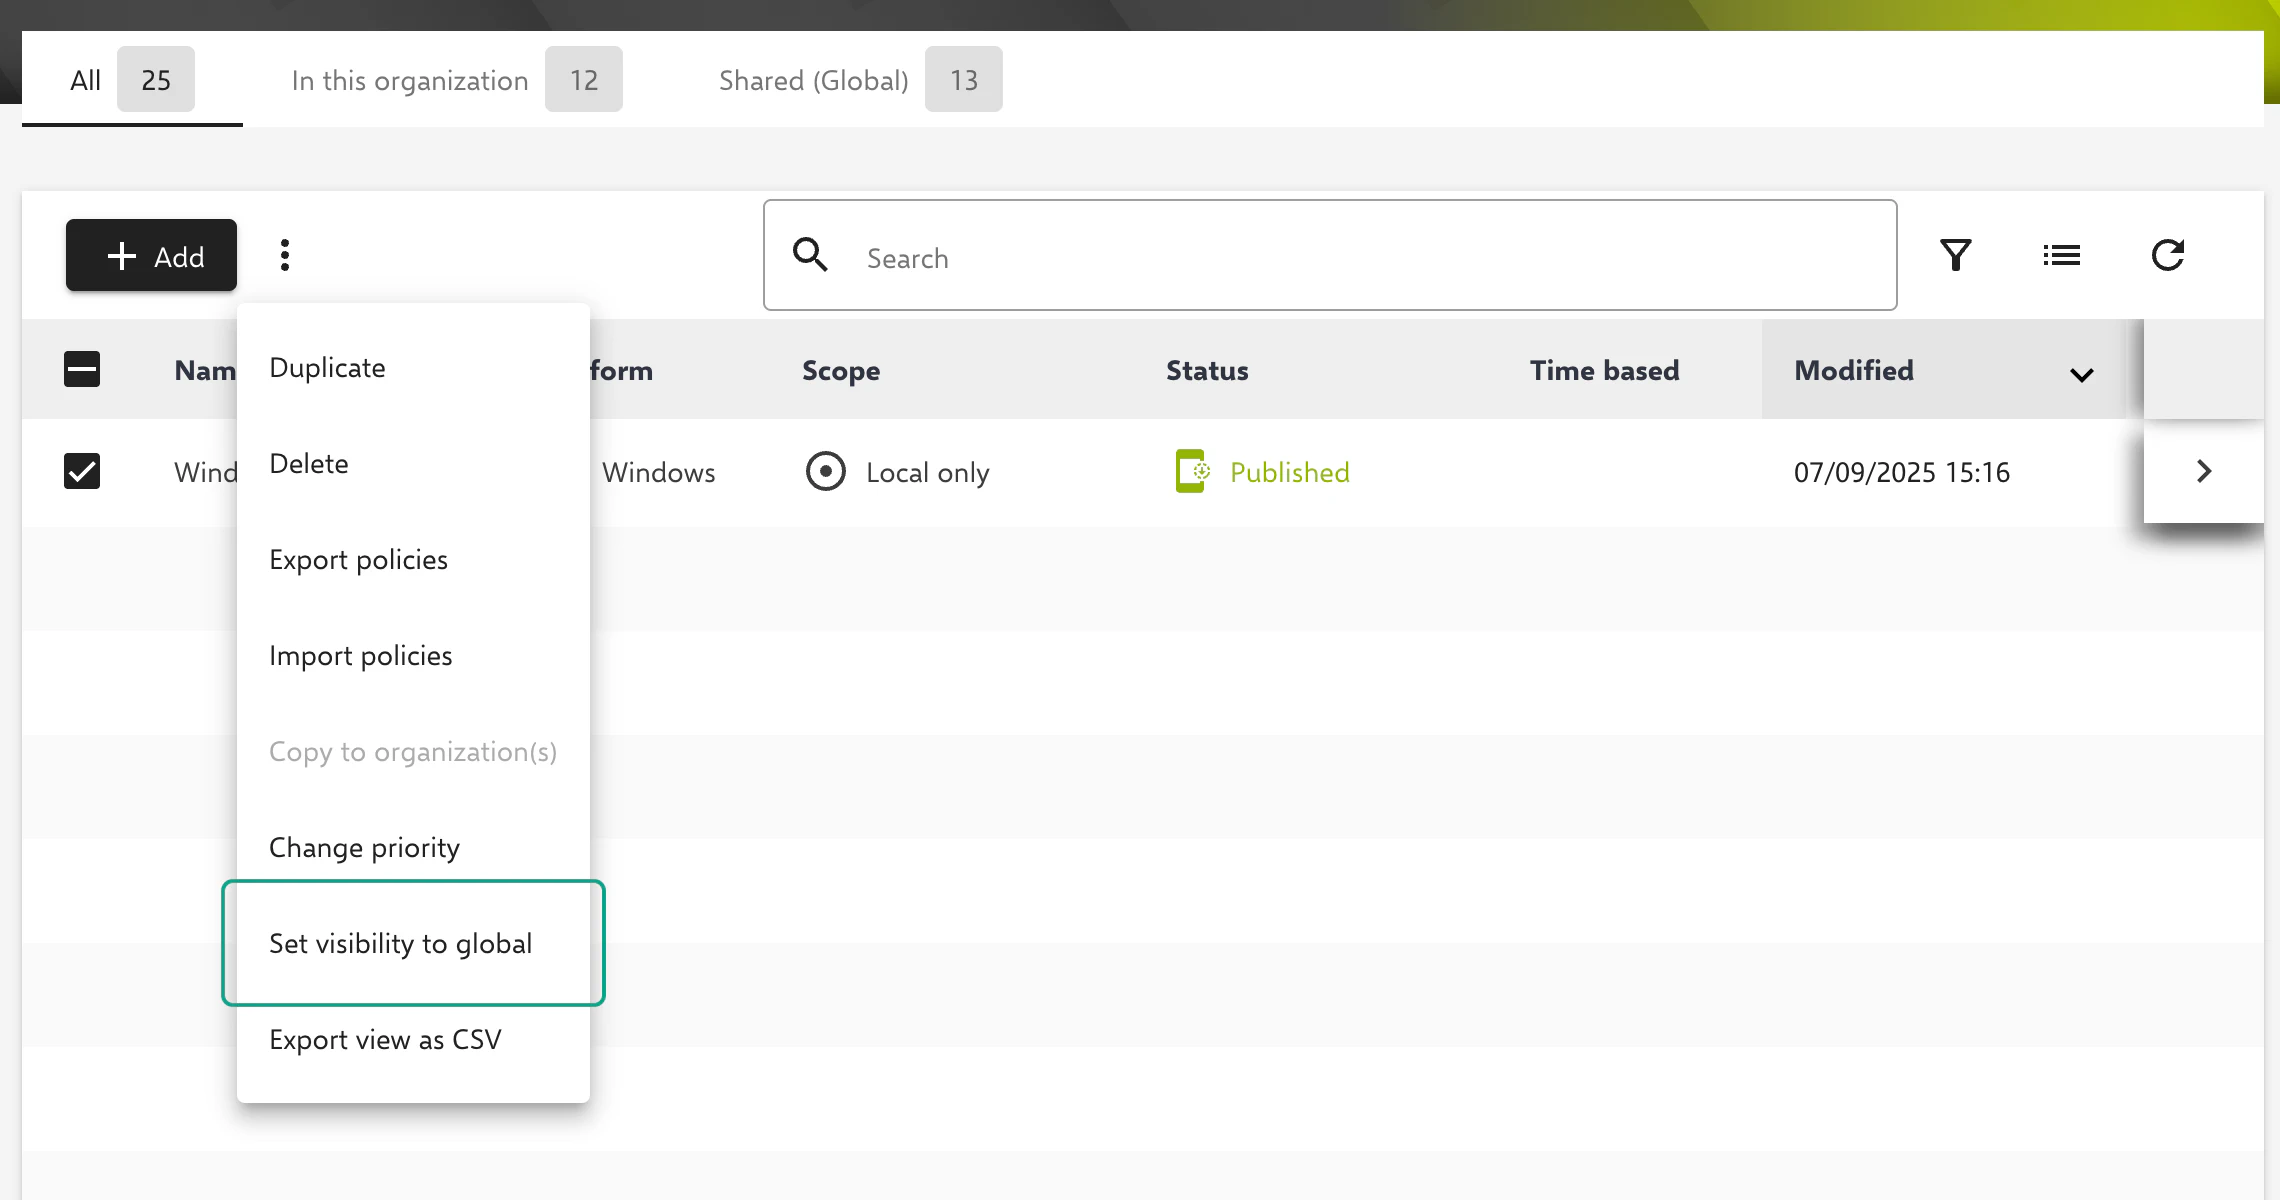
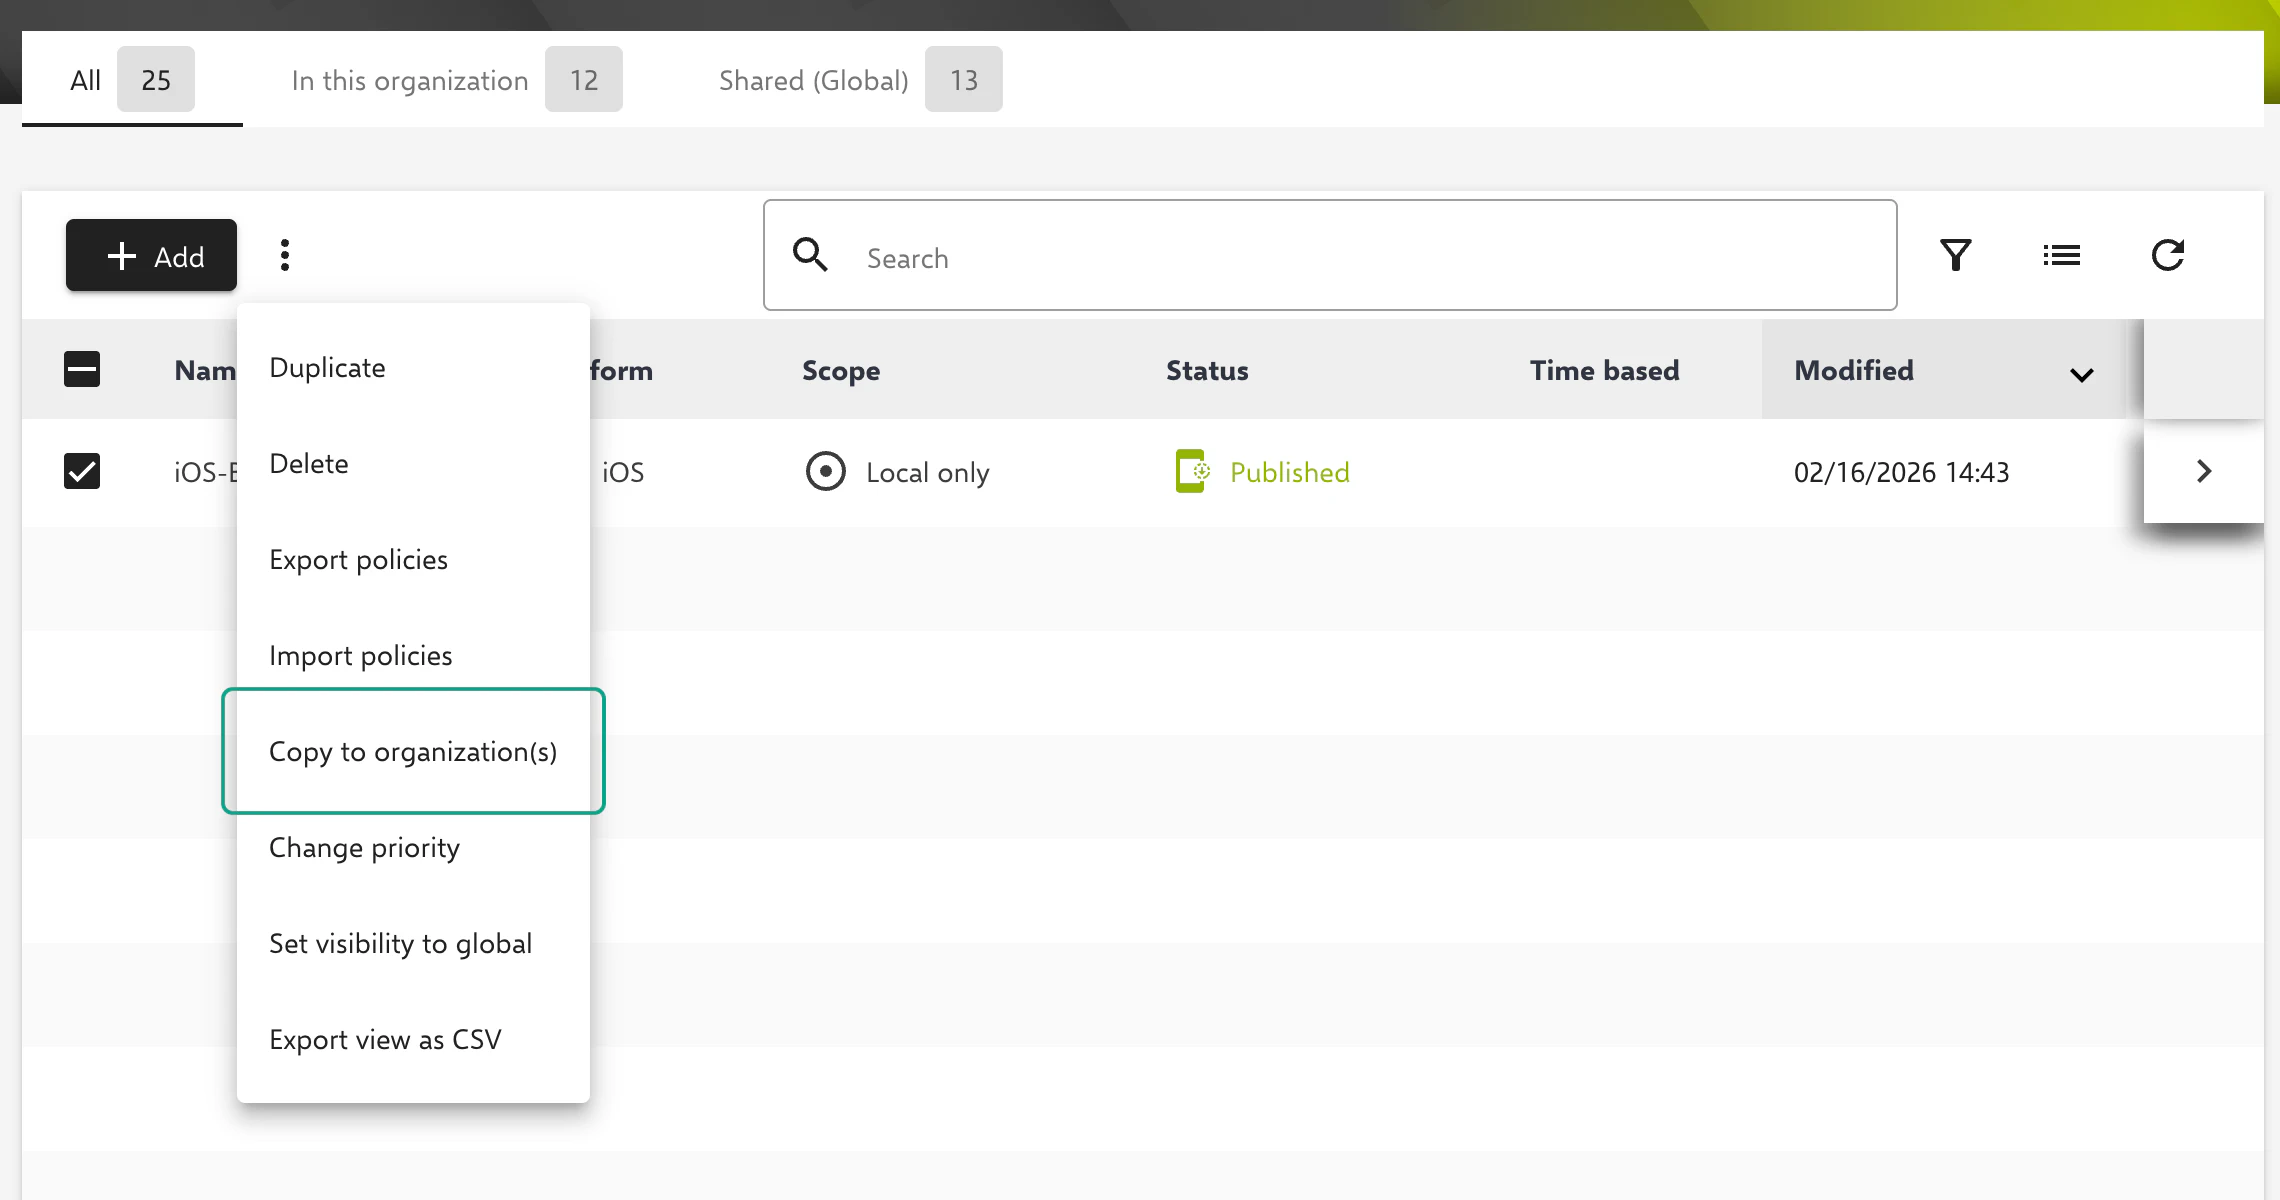
Policies created in the Global Organization can be distributed in two ways:
- Copy to organization(s): copies the policy to one or more organizations. Only available for iOS and tvOS policies.
- Set visibility to global: makes the policy available to all organizations. Available for published policies of all platforms.
Policies made globally available are read-only in the subordinate organizations; changes can only be made in the Global Organization. Global policies take precedence in the prioritization.
Global provision of scripts
Scripts created in the Global Organization (PowerShell scripts for Windows and shell scripts for macOS) can be made available read-only in all subordinate organizations. This works in a similar way to the publication of policies or apps. This is done via the three-dot menu of the script entry in the table using the Set visibility to global function.
System-wide LDAP configuration
The LDAP → configuration can be made here in the Settings and an organization-specific mapping can be made. The advantage is that the LDAP provider only needs to be configured centrally once.
This configuration can be set for user accounts, groups, classes, teacher and student accounts as well as teacher and student groups in the Map objects to organizations area. The mapping filters only distribute objects that are already covered by the import filters of the LDAP configuration.
The Sync unmapped objects to this organization option determines what happens to objects that match no mapping: If it is enabled (default), they are synchronized to the organization containing the LDAP configuration. If it is disabled, they are not imported and are reported as synchronization errors.
Moving devices to other organizations
Via the Move to button in the device list of the Global Organization, iOS/iPadOS, tvOS, macOS, Windows and Android Legacy devices can be moved to other organizations. This is not possible for other platforms (including Android Enterprise, ChromeOS, Linux, visionOS, watchOS). The executing user’s role must include the permissions Inventory (Update) and, as of Relution 26.5.5, additionally System-wide inventory (Read) under Devices.
Moving removes user- and organization-specific data from the device, including the assigned user, device groups and certificates. Only policies that have been made globally available via the global organization will be retained on the devices.
Global Applications
Native apps can be distributed to other organizations via the global organization. In simple terms, this involves creating a link to the app in the child organizations. This saves database/memory resources and considerably simplifies the deployment of the app.
Apps created via an Apps and Books account (VPP in the portal) of the global organization automatically replace existing apps in other organizations.
Requirements
- To distribute the desired app, access to the global organization must be possible. It can be recognized by the globe icon in the organization switcher in the upper right corner, usually also by the name Global.
- An uploaded native app or a Google, Apple or Windows store app that has not yet been distributed globally:
- iOS: .ipa
- macOS: .pkg, .dmg
- Android: .apk
- Windows: .msix, .msixbundle, .appx, .appxbundle, .msi, .exe
- The app has at least one version in the Release status. Otherwise, the Set visibility to global function is disabled (hint Selection contains unreleased apps).
- The app must not already be available globally.
Execution
In the Page Navigation on the left under
Apps→App Store, the mouse pointer is moved over the desired native app.The 3-point menu next to the app name is clicked.
The Set visibility to global option is selected.
For apps that are already (partially) assigned, a dialog window with conflicts and notes may appear.
This action cannot be undone. The following apps already exist in other organizations. If they are made global, the apps in the other organizations will be replaced and deleted. The apps to be made globally available are then selected in the dialog.
This process may take some time.
The app is then shown as Shared in the Scope column. In child organizations it appears as From Global.