 Customer Hub
LDAP Configuration
LDAP providers for user, group and class import can be configured directly via the Relution Portal. The form contains the usual configuration parameters, which can be verified with several functional tests. A restart of the Relution service is not necessary when configuring via the portal, so changes and reconfigurations do not interrupt operations. Configuring LDAP synchronization requires some knowledge of the subject; an LDAP browser that displays attributes correctly is recommended. For Windows, the Softerra LDAP Browser and for Linux or macOS the Apache Directory Studio have proven themselves. Both tools are free of charge.
Basics
LDAP is configured under Settings → LDAP synchronisation.
Multiple LDAP providers can be set up per organization. The mail addresses of the users in Relution must be unique. Otherwise, errors may occur and some user accounts cannot be created.
A new LDAP provider is created via Add.
A manual synchronization can be started at any time: in this list via Start synchronization for the selected provider, and in the lists of users, groups and classes via One-time LDAP synchronization. The detail page of a provider shows the result of the last synchronization for each type (users, groups, classes).
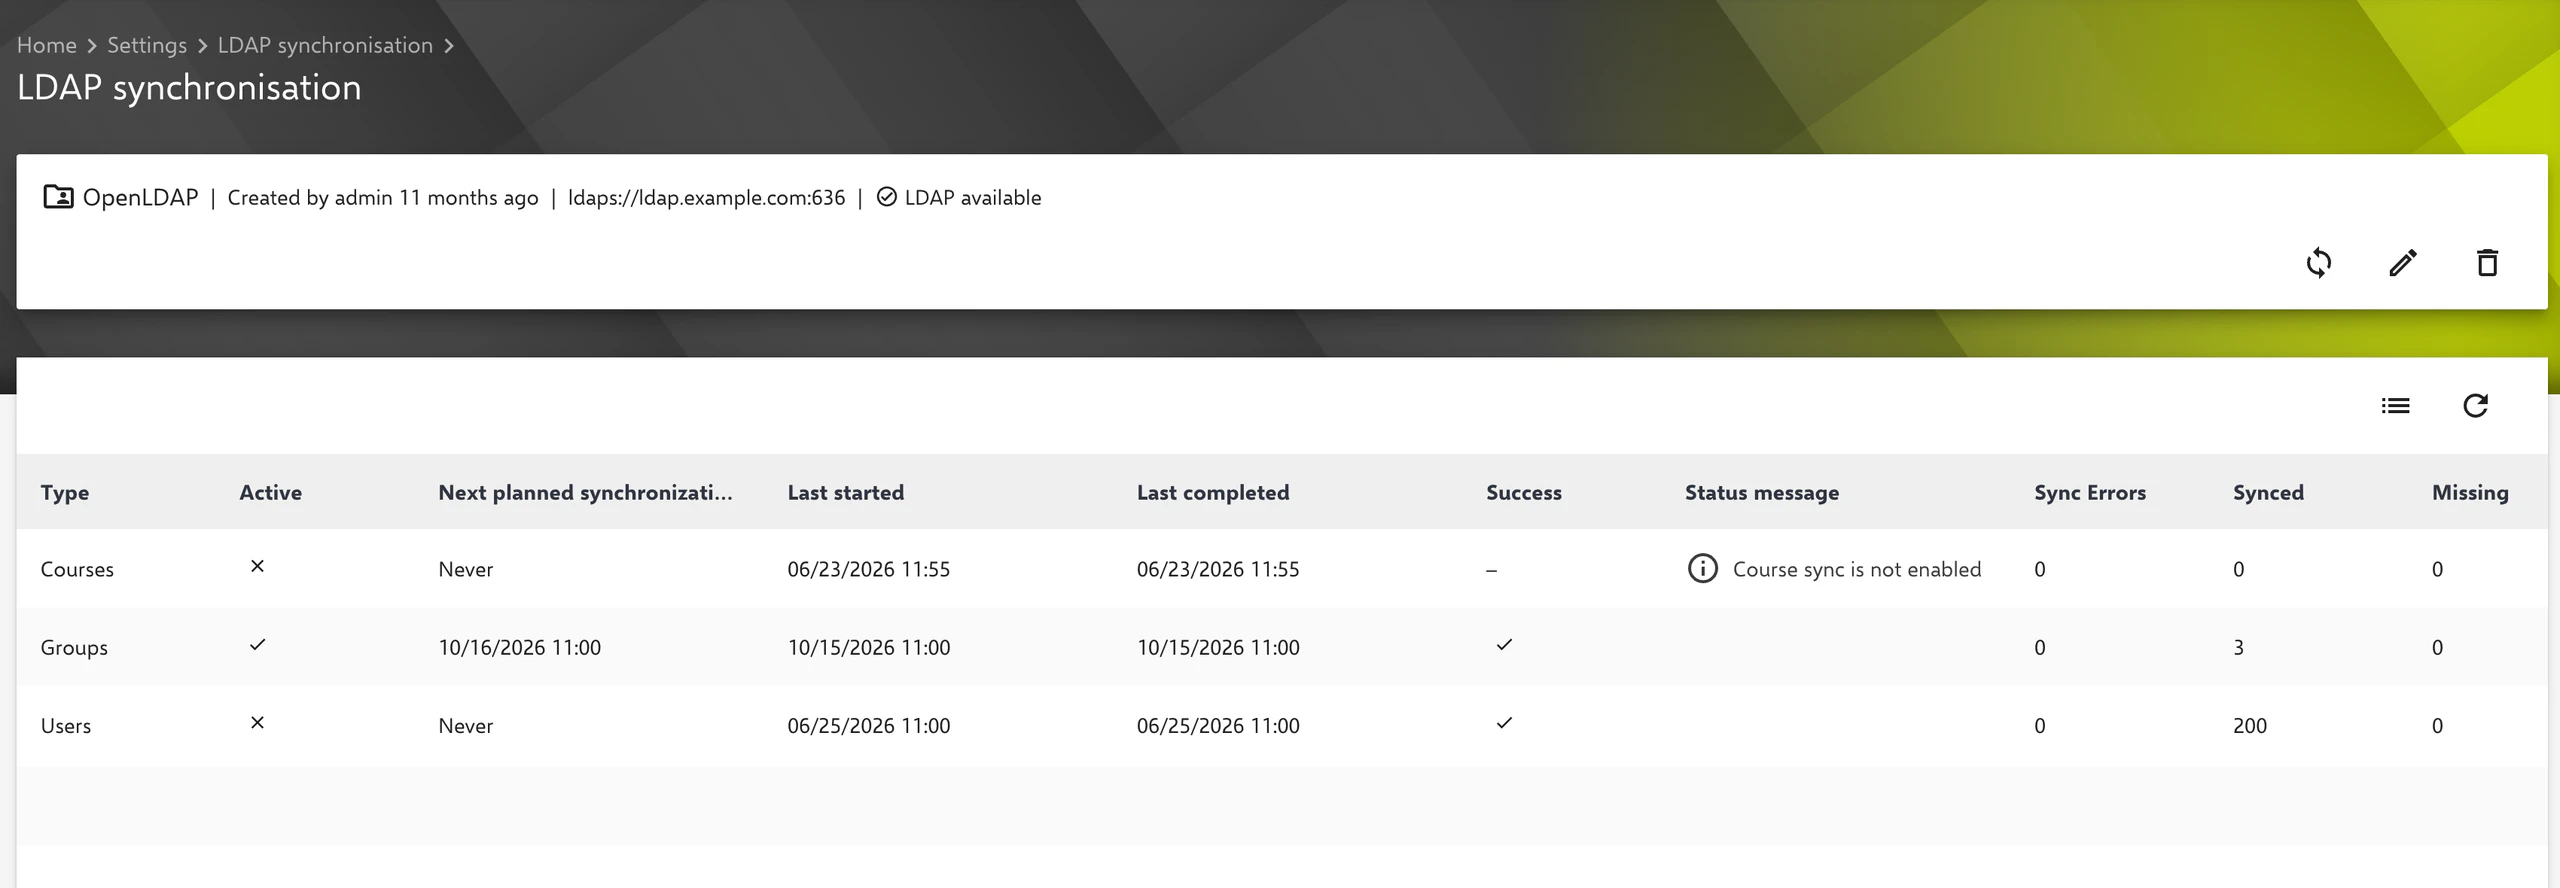
Basic configuration
The configuration form is divided into several levels. Not all parameters are always required for a given case. Some fields already contain examples that suggest the syntax.
LDAP synchronization
First, a name is assigned to the LDAP provider. A short and meaningful name is recommended.
Server settings
- LDAP Server URLs: The URL of the LDAP server is entered and confirmed with
Enter.
If LDAPS is used and the server does not have a trusted certificate, the certificate can be stored under Trusted server certificates so that Relution classifies it as trusted. Alternatively, Trust all certificates makes Relution accept any server certificate. The portal points out the security risk; explicitly stored certificates are preferable.
The connection is checked with Test network connection. The connection attempt should be successful before continuing with the configuration.
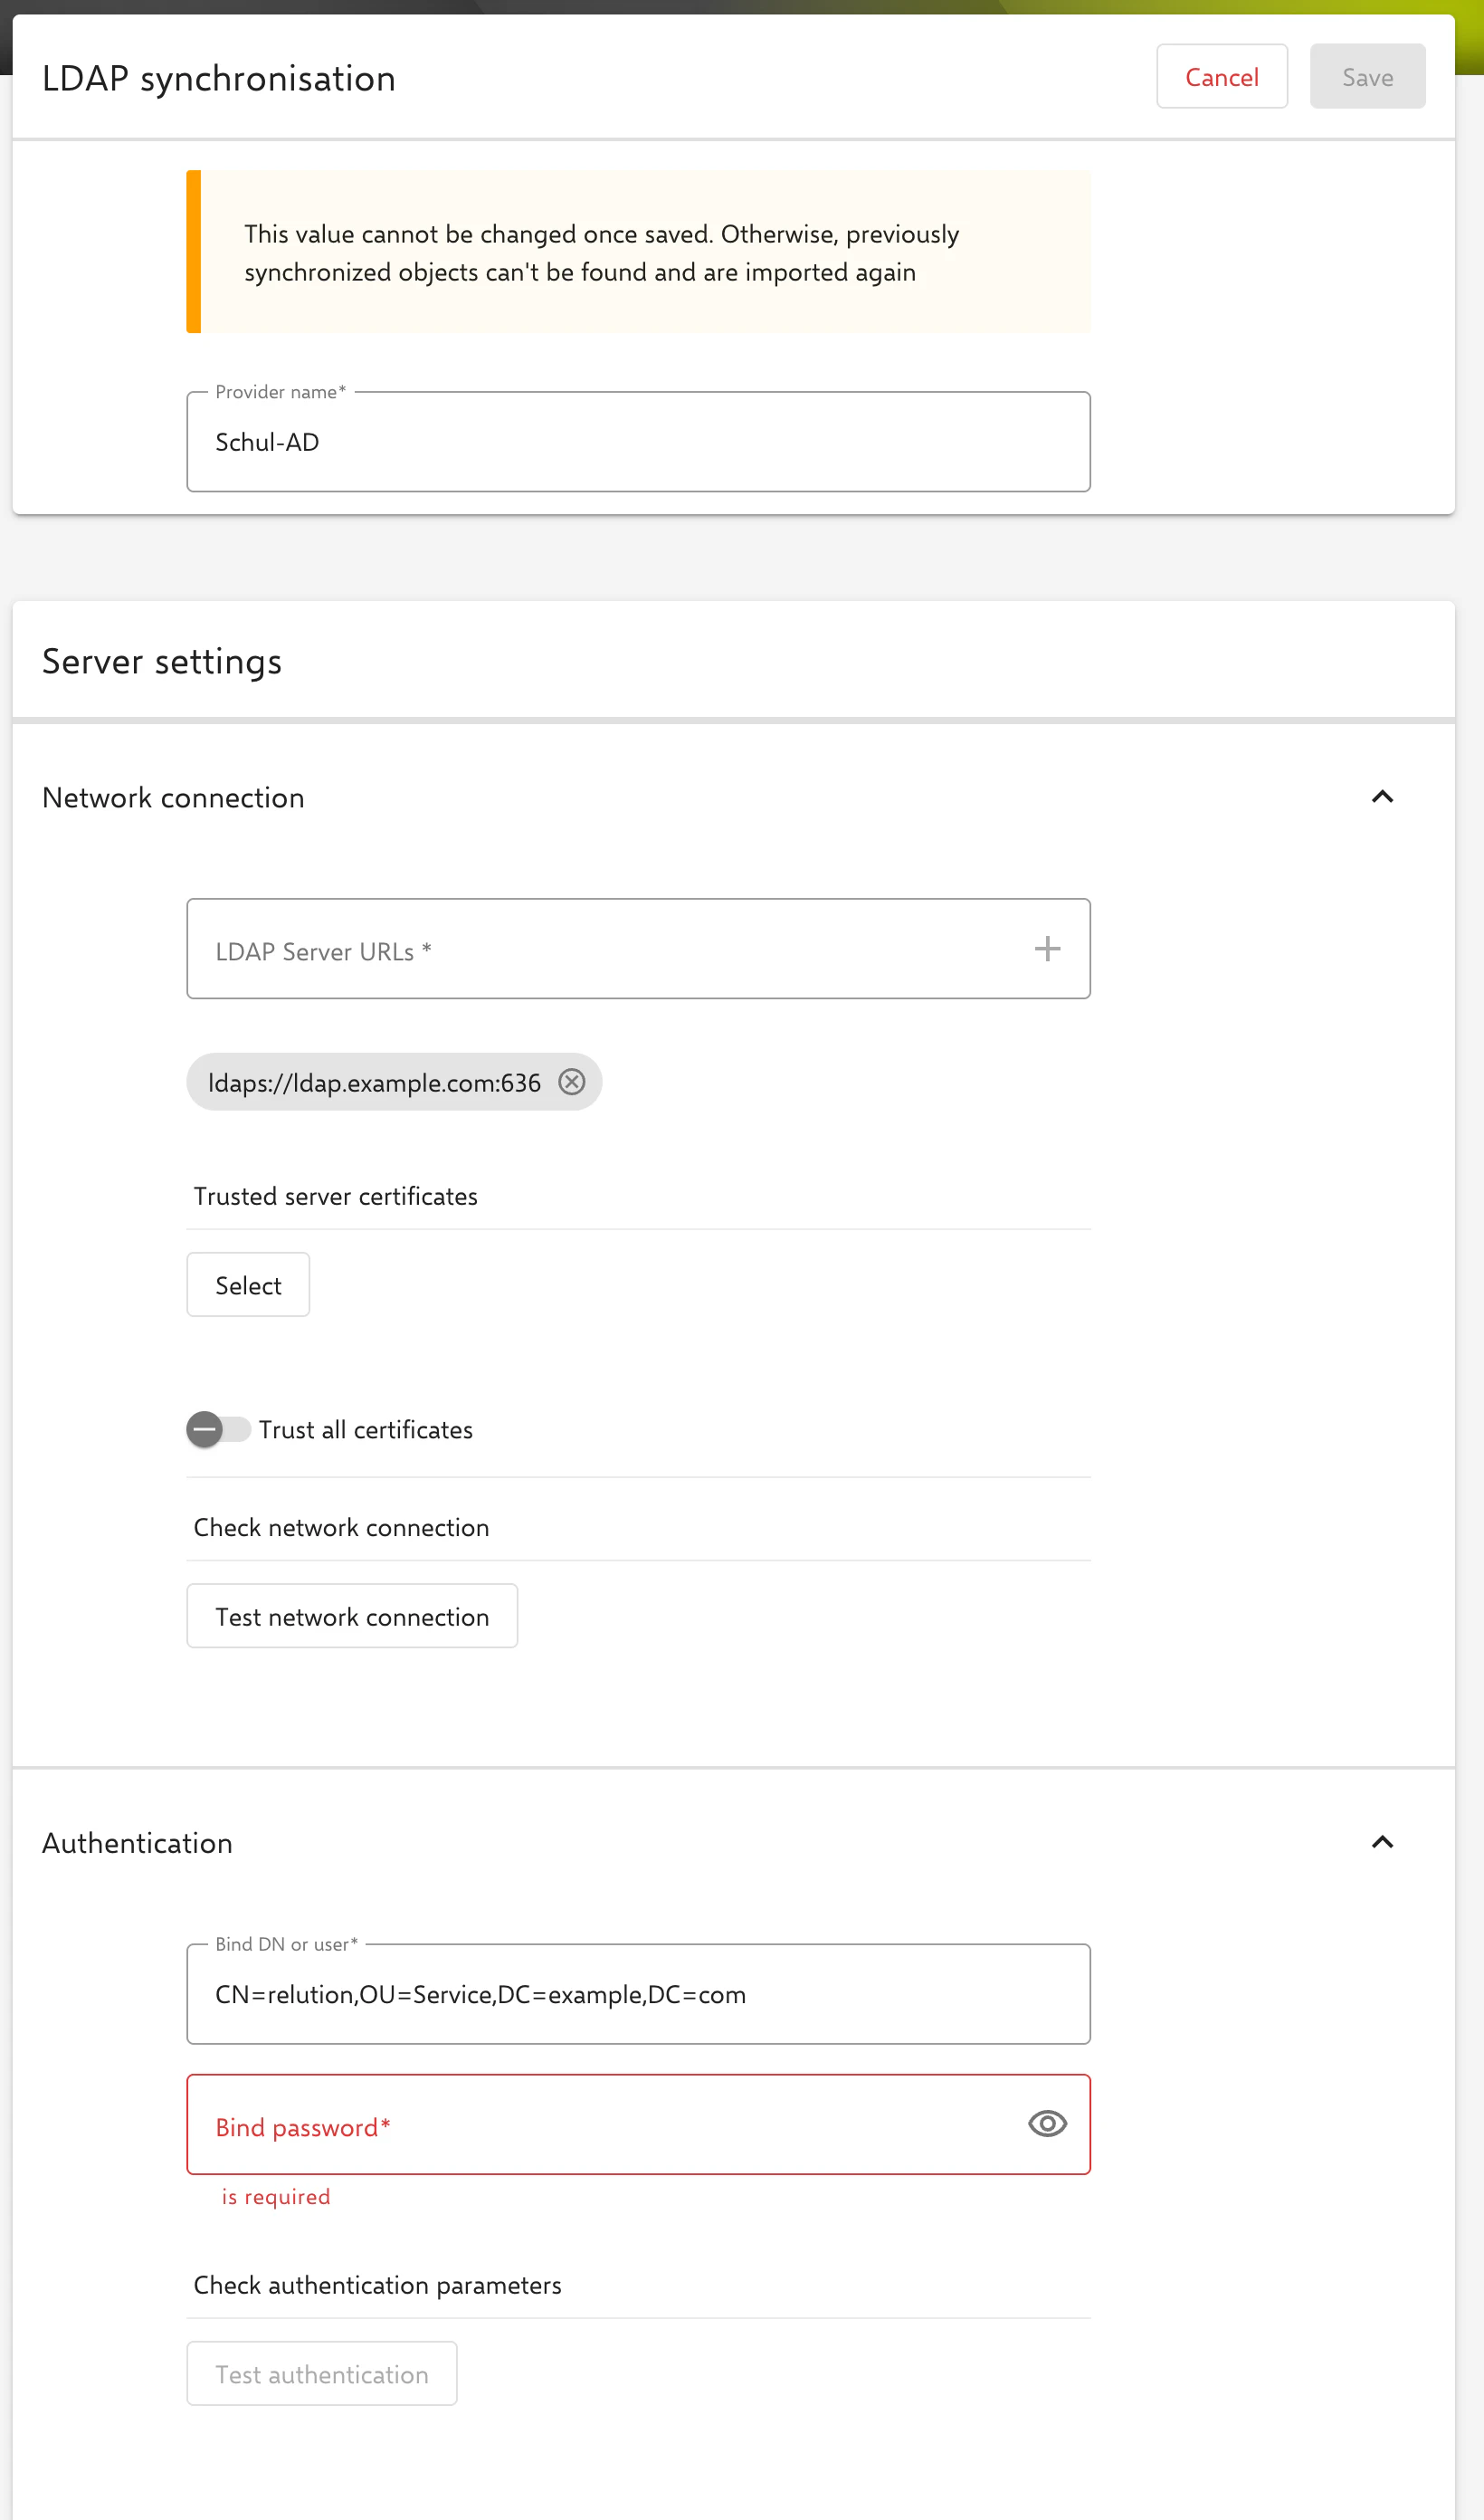
Authentication
- Bind DN or user: Username with read permissions in LDAP. Ideally, the Distinguished Name (DN) is used here.
- Bind password: The corresponding password. For a provider that has already been saved, the field is left empty to keep the existing password (hint Leave empty to keep existing password).
The credentials are checked with Test authentication.
As of Relution 26.5.5, the stored password is only kept as long as no URL has been added or changed under LDAP Server URLs; removing or reordering URLs has no effect. After a URL has been added or changed, Relution rejects saving and all tests except Test network connection with the notice that the connection endpoint has changed. When saving and for Test authentication, Bind password is additionally marked as a required field. In this case, the password is entered again.
Base DN
After a successful Test authentication, the base DNs reported by the server are offered in the Discovered base DNs selection; the first entry is preselected. Use discovered base DN as base DN copies the selected entry into the Base DN field. Any necessary changes can be made at any time.
Search criteria for users
- User search base (Organizational Unit): The search base for users, relative to the base DN, for example
OU=users. - User search filter: Conventional LDAP search filters are used here. Relution always uses the placeholder
%vfor user input. For example, a simple search filter for users could be(&(cn=%v)(objectClass=person)). - User search scope: Configures how deep in the path user accounts are searched with the corresponding search filter. Selecting Subtree may result in a large number of hits.
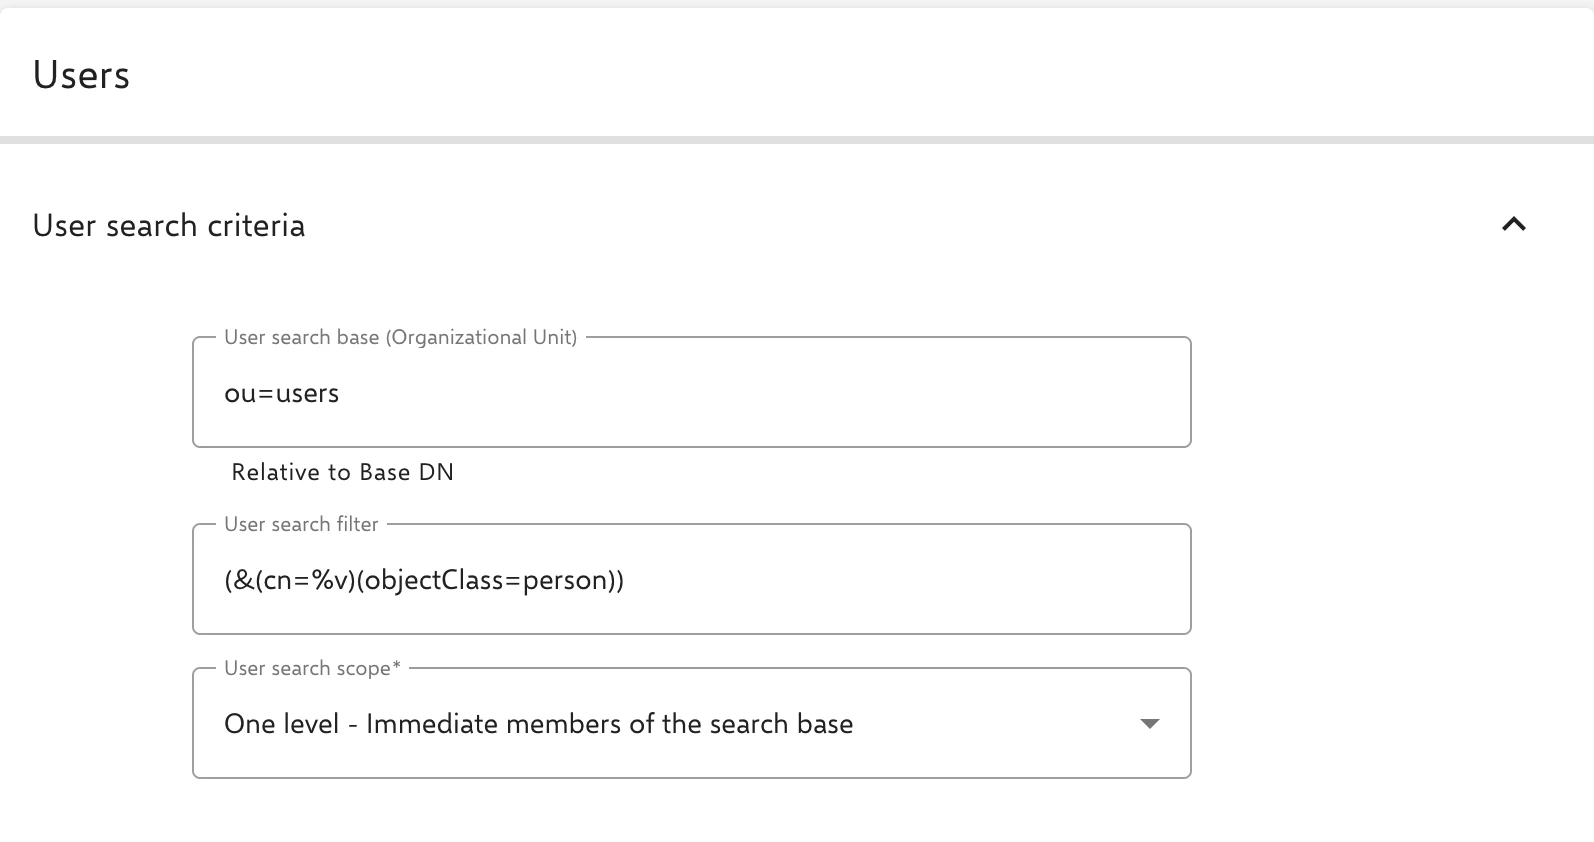
Manual mapping for users
After the connection is established, Relution checks which type of LDAP it is, for example OpenLDAP or an Active Directory. The appropriate fields are then preconfigured via an auto-mapping. This function can be partially or completely overridden by enabling Manual user attribute mapping.
For example, setting a foreign key is recommended. This is useful when users change their name: the user account can still be identified, and the name and mail address are just updated without creating a new account in Relution.
User synchronization
Test user import checks whether the users can be imported and whether the filters return the correct results.
In addition, Periodic user import can be enabled. This is an automatic synchronization that runs every 24 hours at the selected Synchronization time. If periodic import is disabled, users matching the search filter are still imported when they log in or when they are assigned to an enrollment.
A manual synchronization can be started at any time (see Basics →).
Synthetic group: This is a group that is automatically created by the LDAP sync. All users imported via the LDAP provider – during the scheduled synchronization or at their first login – become members of this group.
- The group name consists of the organization’s Unique name in uppercase letters and the entered value. With the default value
LDAP, this results, for example, in the groupMYORG LDAP. - If the field is left empty, no synthetic group is created.
- Since permissions can be assigned to LDAP groups, the synthetic group is suitable for assigning a role to all LDAP users together, e.g. for Multi-factor authentication →.
- The group name consists of the organization’s Unique name in uppercase letters and the entered value. With the default value
The option When an LDAP user is not found can only be edited while Periodic user import is enabled (default: Do nothing). It also applies when a user still exists in LDAP but no longer matches the search criteria. Three reactions are available:
- Do nothing: The user remains in Relution. However, the account can no longer be used for login because the LDAP provider refuses authentication.
- Disable the user in Relution: This is the recommended setting, as user accounts remain associated with devices and no data is lost if the accounts are accidentally no longer found, for example after renaming a group in LDAP that a filter then no longer finds. As of Relution 26.5.5, the devices of deactivated users remain manageable but no longer act with the user’s permissions. For example, the Teacher App on the device of a deactivated teacher lacks the corresponding permissions. Once the user is reactivated, the previous state applies again.
- Delete the user from Relution: Users that are no longer found by the importer are removed directly from the database, regardless of any links to devices, groups or classes.
Search criteria for groups
- Group search base (Organizational Unit): The search base for groups, relative to the base DN, for example
OU=groups. - Group search filter: Conventional LDAP search filters are used here. Relution always uses the placeholder
%vfor user input. For example, a simple search filter for groups could be(&(cn=%v)(objectClass=groupOfNames)). - Group search scope: Configures how deep in the path groups are searched with the corresponding search filter. Selecting Subtree may result in a large number of hits.
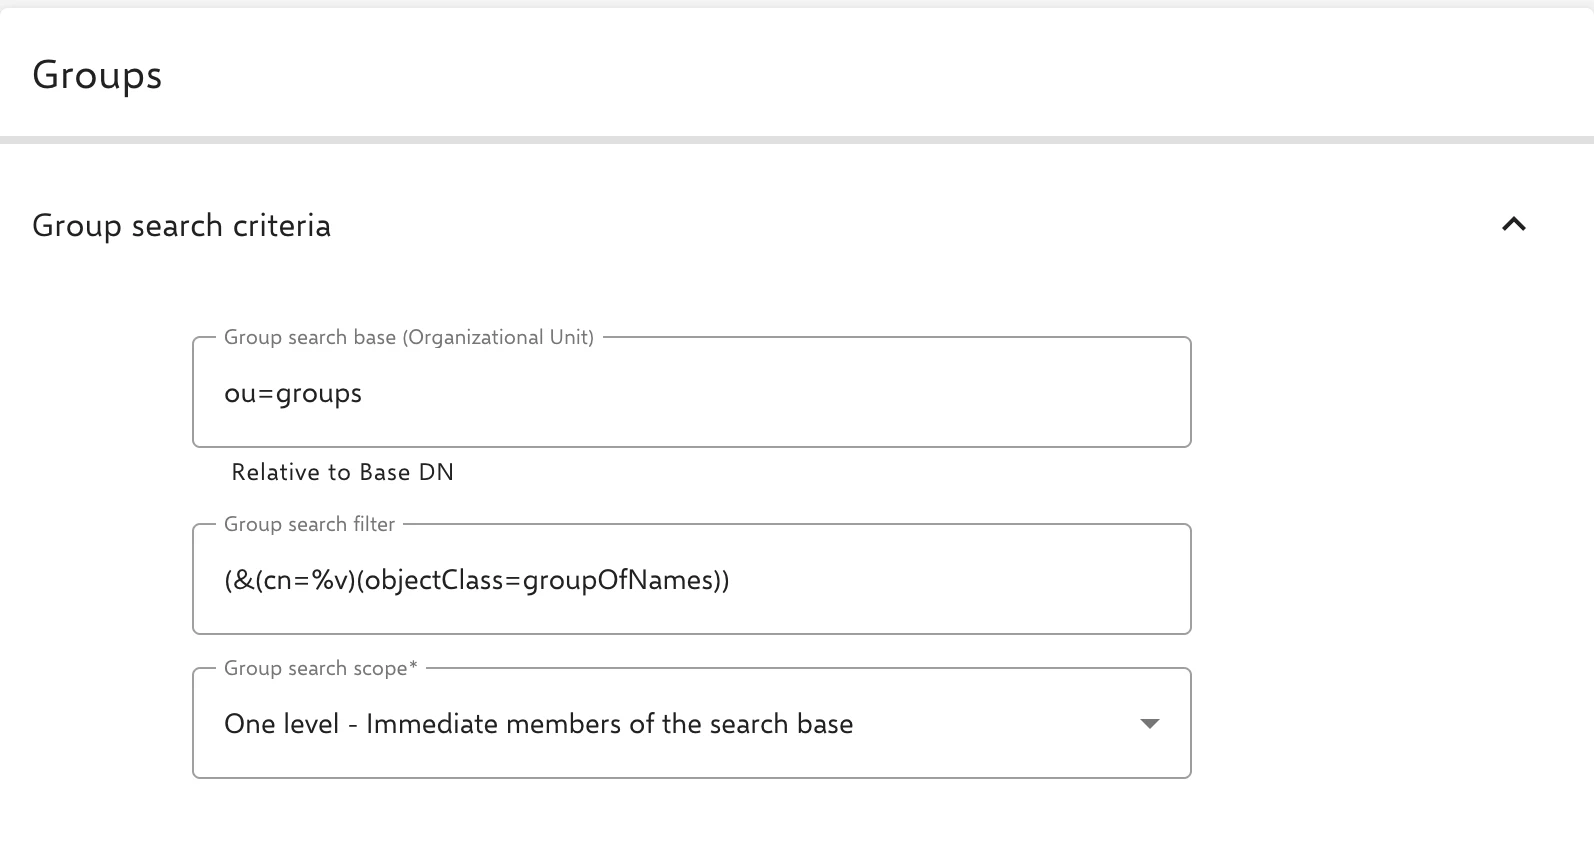
Manual mapping for groups
The manual mapping (Manual group attribute mapping) behaves for groups as it does for users.
Often, the entryUUID field is used for the Foreign key (UID) and the member field for Member. The attributes can be checked with one of the LDAP tools recommended above or via the console with ldapsearch.
Group synchronization
Test group import checks whether the groups are found.
For LDAP groups to be imported, Import groups of imported users must be enabled. Relution then imports all groups in which synchronized users are members and that match the group filter, including the groups these groups in turn belong to. If the toggle is disabled, only synthetic groups are created.
In addition, Periodic group import can be enabled: every 24 hours at the selected Synchronization time, all groups matching the group filter are imported, even without imported members. Periodic group import and the time can only be set once Import groups of imported users is enabled.
The import is always user-centric: groups do not pull in additional users. Members of a group are only imported if they match the user search criteria themselves.
Education
LDAP synchronization can also be used to create classes that are displayed in the Education section of the menu and can be used for the Relution Teacher Console or in Apple Classroom. Classes to be created in Relution are group objects in LDAP. They must contain at least one teacher or teacher group and at least one student or student group.
Search criteria for classes
The configuration here is similar to that for users and groups: a search base containing the classes and a corresponding search filter are defined. The search scope is configured as usual via the drop-down menu.
The configuration can be checked with Test class import. Classes are only created later if they contain at least one teacher or teacher group and at least one student or student group. Groups only count if they are found via the search criteria for teacher and student groups.
Search criteria for teachers and students
Here, the configuration also consists of the search base and a corresponding filter. Often, the individual user types are defined by group memberships. Search filters can look like this, for example:
- Teachers:
(&(memberOf=CN=all-teachers,OU=groups,DC=school,DC=local)(objectClass=person)) - Students:
(&(memberOf=CN=all-students,OU=groups,DC=school,DC=local)(objectClass=person))
The filters can be checked with Test teacher import and Test student import.
Search criteria for teacher and student groups
Groups can be imported as members of classes. For this, one filter each is configured for teacher groups and student groups. These filters can be used in addition to or instead of the filters for teachers and students. If the automatic import of education data is enabled, at least one of the two filters (user or group filter) must be set for each role. Search filters can look like this, for example:
- Teachers:
(&(cn=teacher*)(objectClass=groupOfNames)) - Students:
(&(cn=students*)(objectClass=groupOfNames))
The filters can be checked with Test teacher group import and Test student group import.
Synchronization of education data
The automatic import of education data is configured here as well: with Periodic education import, classes are synchronized every 24 hours at the selected Synchronization time. Classes that are no longer found during a successful synchronization are deleted in Relution.
Organization mapping (Global and Meta)
In the Global Organization and in meta organizations, LDAP providers can be configured to synchronize users, groups and classes into individual organizations via mappings (Map objects to organizations). For each target organization, filters can be set for users, groups, classes, teachers, teacher groups, students and student groups, each as an LDAP filter or a DN filter. The result can be checked with Test organization mapping.
The filters of a mapping only distribute objects that are already found via the import filters. By default, only objects that match a mapping are synchronized; all others are not imported and are reported as synchronization errors. If the option Sync unmapped objects to this organization is enabled under Organization mapping settings, the remaining objects end up in the organization in which the provider is created. If an object matches the filters of several organizations, it is skipped with an error.