 Customer Hub
Multi-factor authentication
Multi-factor authentication, or MFA for short, is a security mechanism that requires users to provide at least two independent verification factors to uniquely identify themselves when accessing an application.
Unauthorized access is made significantly more difficult by the additional authentication method; the security level is thus significantly increased.
MFA and Relution
Relution enables LDAP and local users to activate the additional authentication methods E-Mail (one-time code by e-mail) and Authenticator App in the Relution Portal in addition to specifying user name and password.
This way, the requirement of the German Federal Office for Information Security (BSI) for MDM providers to implement the provision of an additional security level is taken into account.
How is the MFA configured in Relution?
Under Settings → Login Management, an organization or system administrator defines in the Multi Factor Authentication section which MFA methods are available in the organization. By default, E-Mail Authentication and Authenticator Apps (TOTP) are enabled. The setting of the organization a user belongs to applies.
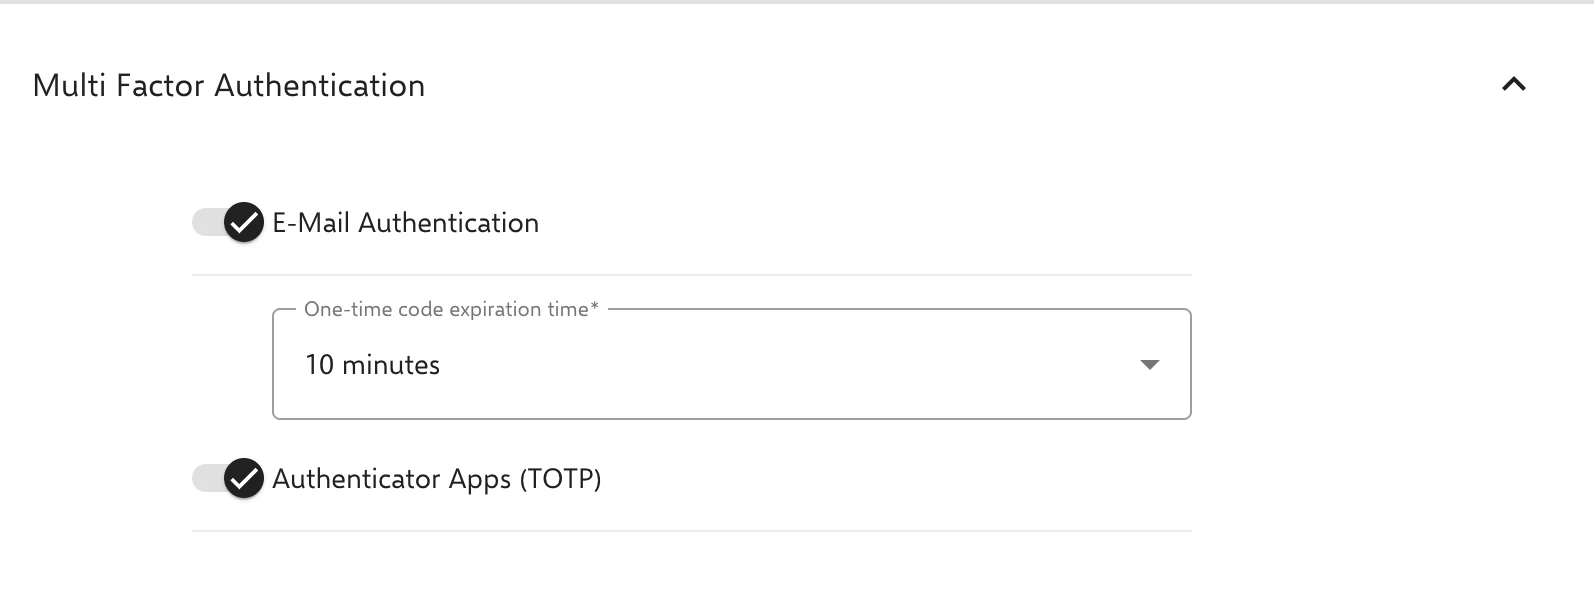
For E-Mail Authentication, the One-time code expiration time is defined: 30 seconds, 1, 2, 5, 10, 15 or 30 minutes, or 1 hour (default: 10 minutes). Authenticator Apps (TOTP) allows signing in with a time-based code from an authenticator app. Each of the two methods can be disabled individually; both can also be active in parallel.
If both methods are disabled, Relution no longer requests a second factor at login – neither for roles with enforced MFA nor for users who have already set up MFA tokens.
Force MFA log in
The Relution Permission system has been extended with the possibility of multi-factor authentication. It is possible to define for a role whether MFA log in is required or not.
If the permission/role with activated MFA login is assigned to a user or a group, an MFA login is mandatory when logging in.
If no MFA method has been set up yet, then the user must do this at the first log in.
MFA does not only apply to logging in to the Relution Portal. As of Relution 26.5.5, the second factor is also requested when logging in to applications that use Relution as Identity Provider →. As of Relution 26.5.6, this additionally applies to logins directly on the device, i.e. logging in to shared devices via the Relution Agent and the user login during Android Enterprise enrollment (see Enrollment options →). The device is only assigned to the user once the second factor has been confirmed.
Enforce MFA for a group
If MFA login is to apply to all members of a group, a role with MFA enabled is created and assigned to the group. Roles from parent groups are also taken into account.
- Under
Users→Permissions, a new role is created via Add, or an existing custom role is opened. - In the Multi-factor authentication section, the option Enforce multi-factor authentication for the role is enabled and applied with Save.
- Under
Users→Groups, the desired group is opened. - Via Manage Permissions, the role is selected and applied with Save.
The Multi-factor authentication section only appears in the role once at least one MFA method is enabled under Settings → Login Management. The default Relution roles cannot be edited; a custom role is therefore required for MFA. The assignment is also possible for groups synchronized via LDAP. Further information on roles can be found in the article Permissions →.
E-mail token
Each user can activate MFA for themselves in the Relution Portal, independently of an administrator. Once an MFA token is set up, the second factor is requested at every login, even without a role enforcing MFA.
In the Relution Portal, the user menu at the top right opens the Profile entry. There, on the MFA Tokens tab, the Add button opens the Add a new MFA token dialog. The tab only exists if at least one MFA method is enabled under Settings → Login Management. After selecting E-Mail, the e-mail address is entered in the next step.
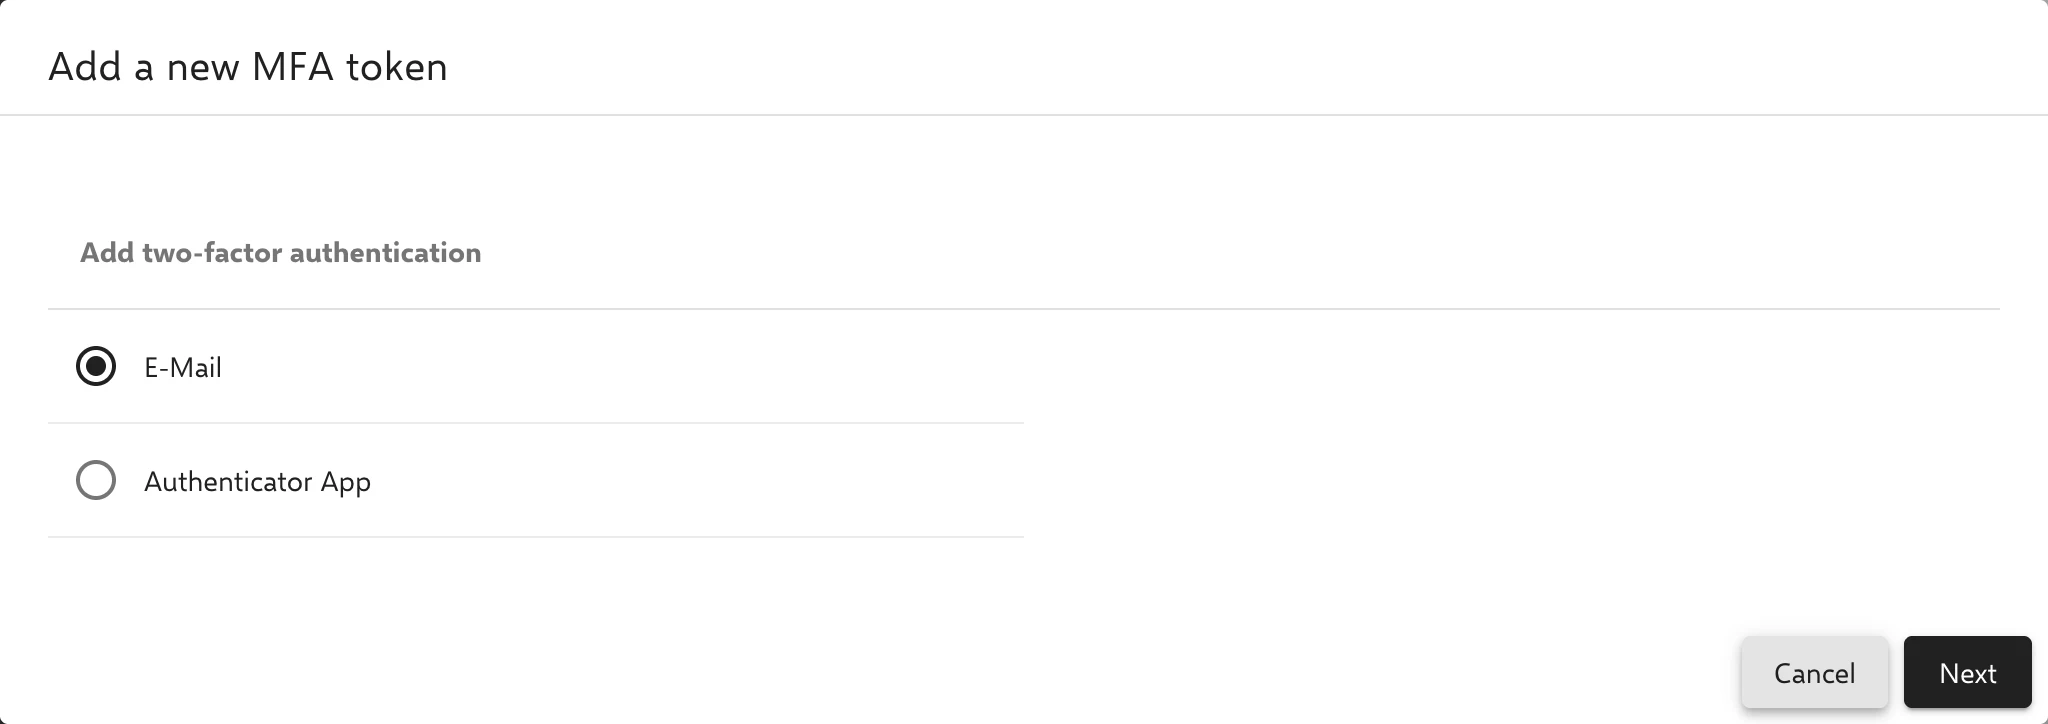
Private as well as user different e-mail addresses can be stored in the system - useful in the school context.
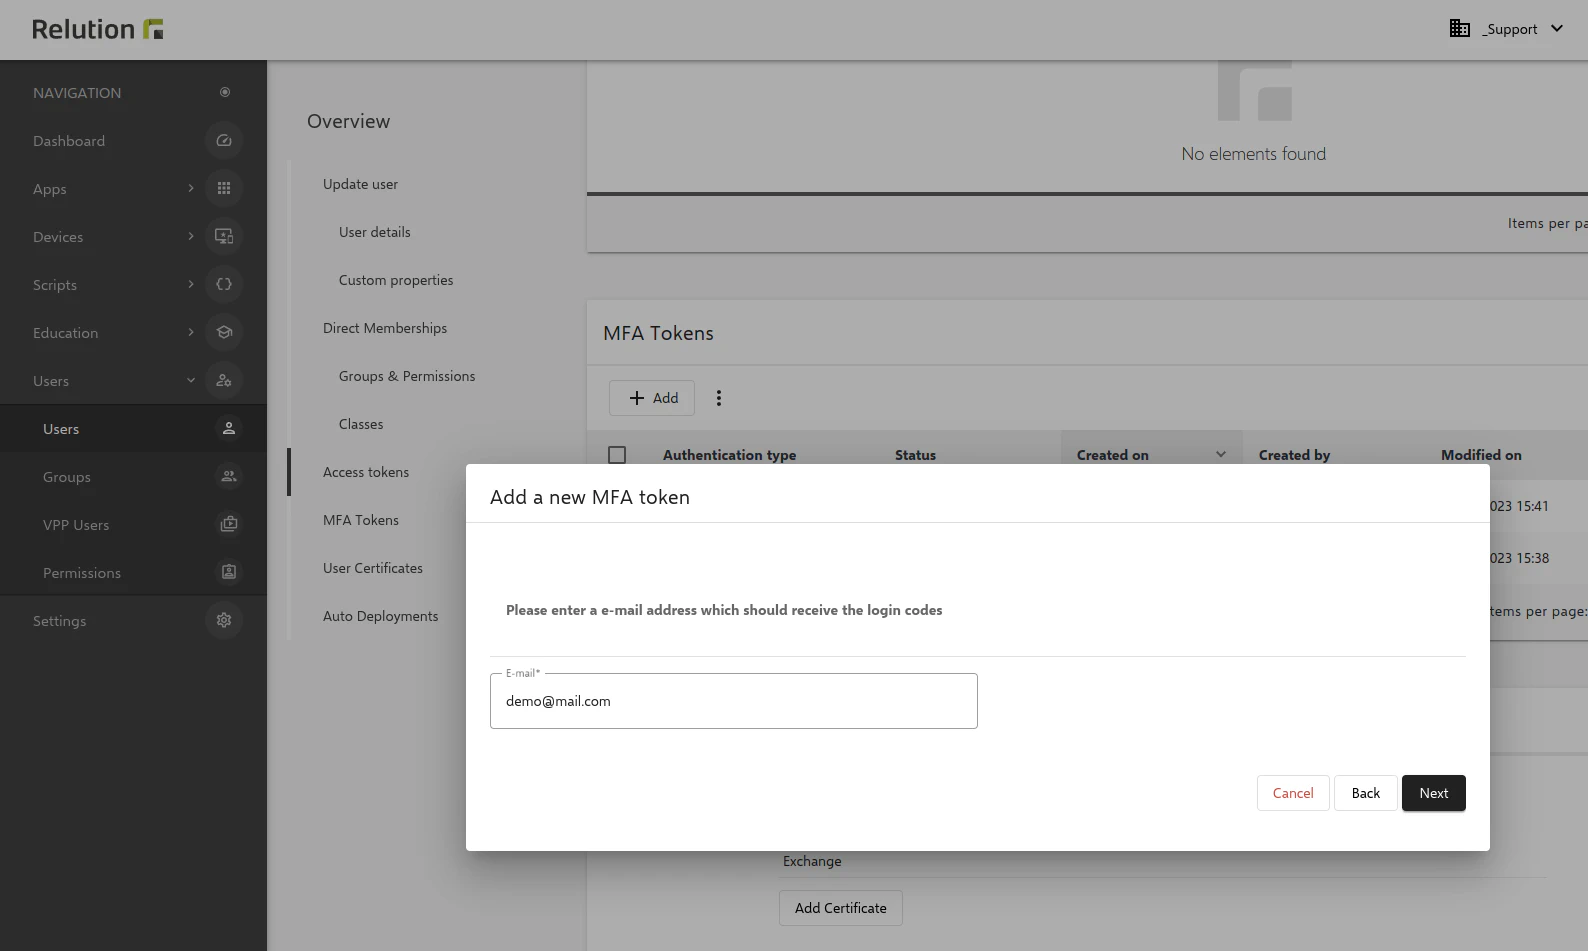
After entering the address, a one-time verification code is sent to the stored e-mail address. It remains valid for the time period defined by the administrator. As soon as the six-digit Verification code from the e-mail is entered, multi-factor authentication is set up. If the setup is cancelled beforehand, the token appears with the status Uncompleted and does not count as an MFA factor.
Any number of MFA factors can be stored in the Relution Portal. If several e-mail tokens are set up, the code is sent to all stored addresses at login. In addition to the e-mail variant, the use of various Authenticator Apps is supported.
If the second variant Authenticator App is selected in the Add a new MFA token dialog, a QR code is displayed, which is scanned with an authenticator app previously installed on the end device.
It is also possible to use a setup key for verification.
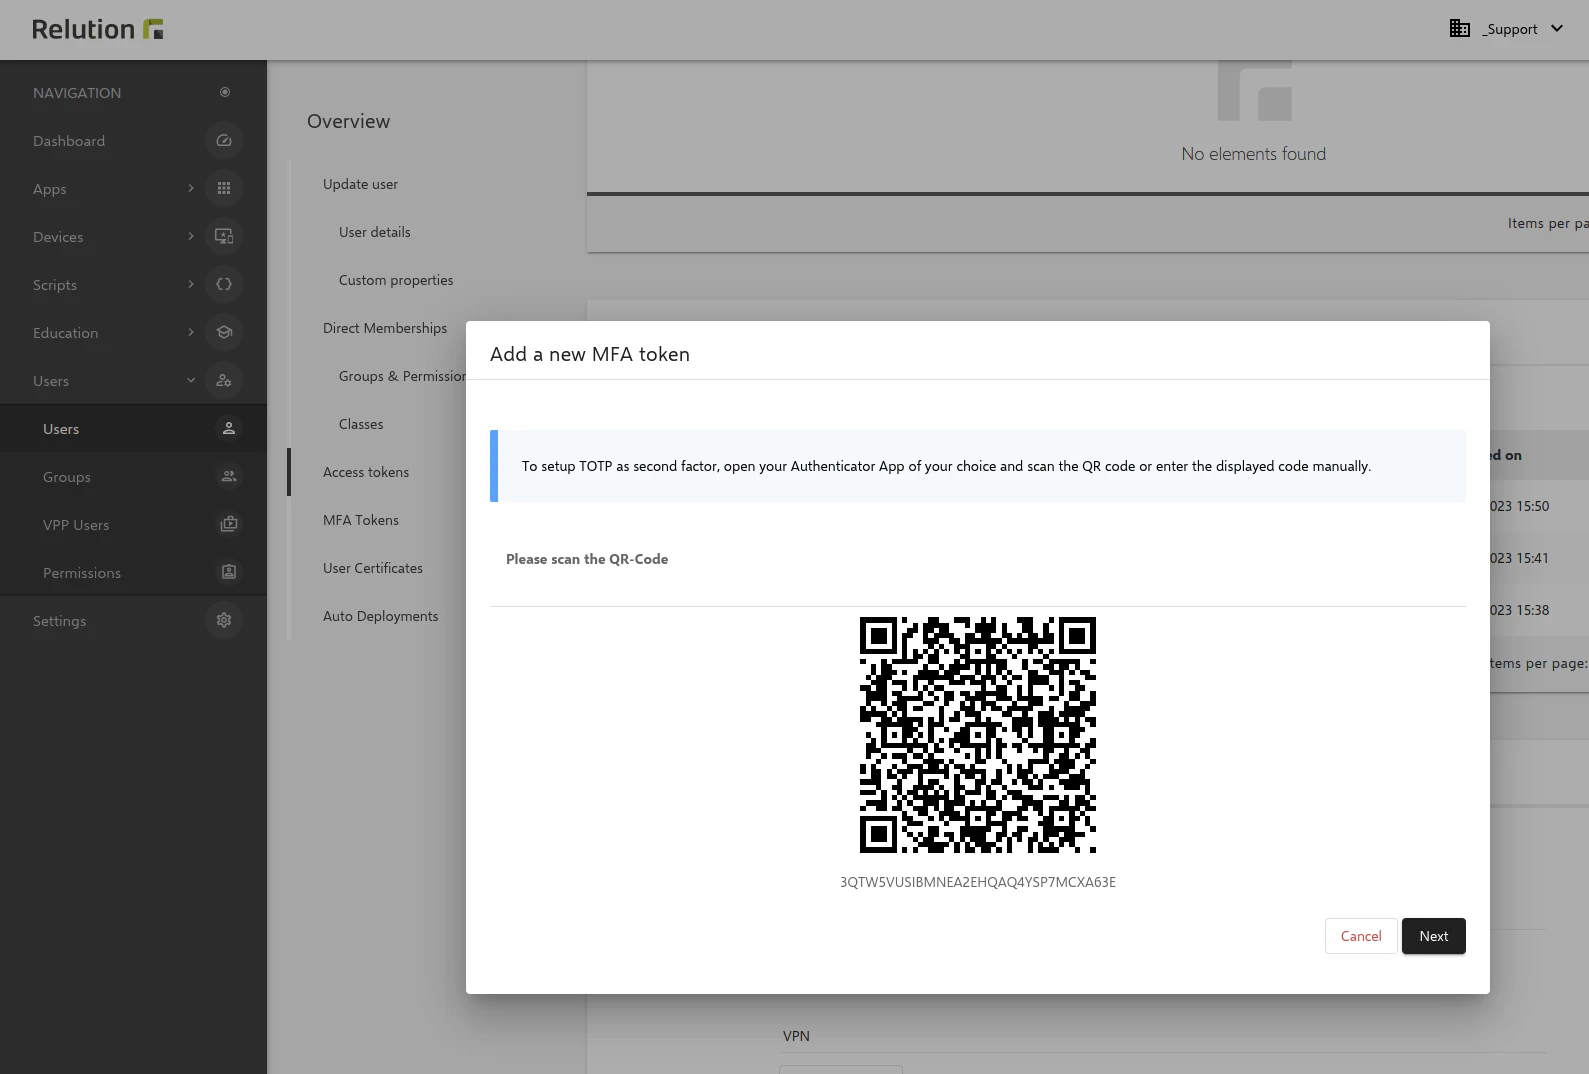
If various Authenticator apps are in use on multiple devices at the same time, the validity of at least one app is checked for a correct login. When using both multi-factor authentication methods, the Authenticator app is primarily queried; the stored e-mail variant serves as a backup. At login, the Use e-mail button (below No access to the Authenticator App?) switches to the e-mail variant; Re-send e-mail requests a new code.
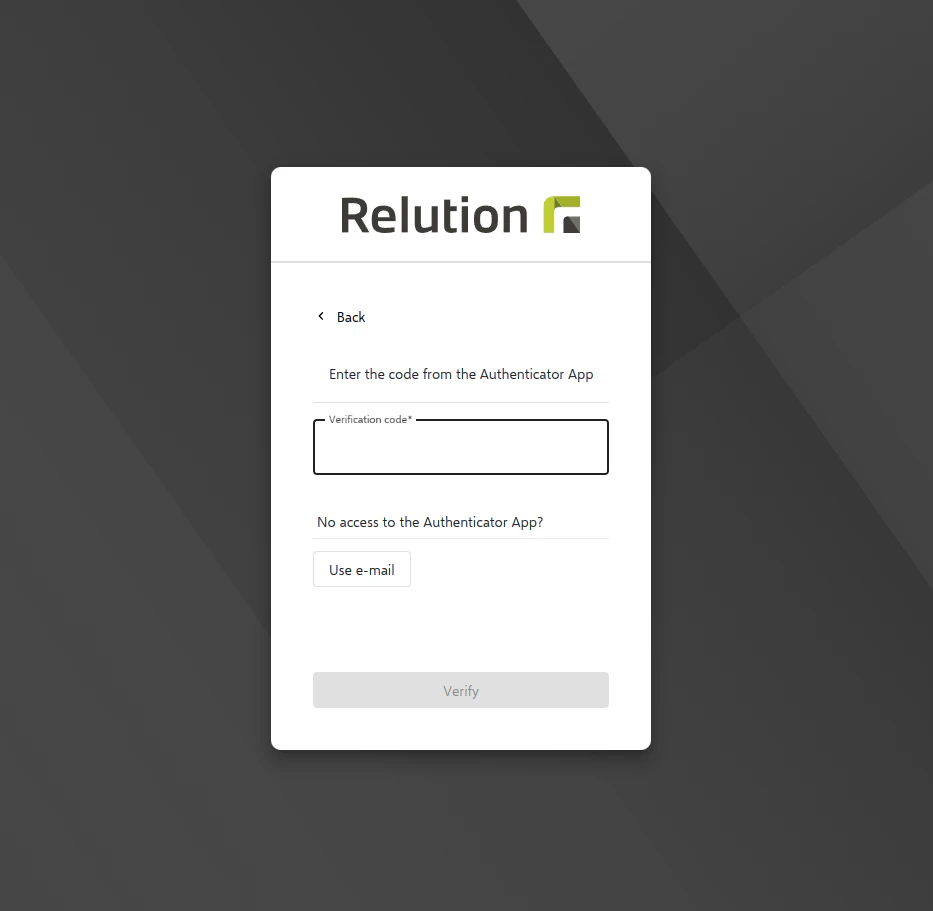
If only the Authenticator app is in use, there is no email fallback.
Delete MFA tokens manually
MFA tokens can be deleted manually by the user in the Profile on the MFA Tokens tab.
If all MFA variants have been removed manually, but MFA is enforced via a role, multi-factor authentication must be stored again the next time the user logs in to the Relution Portal.
What happens if the MFA is lost?
If the user does not have access to email and/or Authenticator app while the MFA is activated, logging into the Relution Portal is no longer possible - going to the Administrator is mandatory.
Under Users → Users, the affected user can be opened and the token deleted in the MFA Tokens section. This requires the permission to delete users. With the permission to create users, MFA tokens can also be added for the user there.
The MFA column of the user list shows whether a user has set up MFA; the filter of the same name distinguishes Configured and Not configured.