 Customer Hub
App Control
Relution provides the App Control configuration. With this feature, Windows Defender Application Control (WDAC) policies can be applied to Windows devices. These policies define which applications are trusted, allowing only those trusted applications to run on the device. The configuration is supported on Windows Pro, Enterprise and Education version 1903 and later.
Microsoft provides all necessary information for WDAC policies in their documentation →.
WDAC policy generation
Microsoft explains the design and creation of WDAC policies in their design guide →.
It is recommended to thoroughly test any WDAC policies before deploying them to production devices via Relution.
Create the needed WDAC policy file
For the generation the WDAC Wizard → and the example base policies → can be used.
The Windows Defender Application Control (WDAC) Policy Wizard generates two files when used for policy generation: an XML file and a CIP file. The MDM interface of Microsoft requires the policy as a binary file. The CIP file is already in this binary format and can be uploaded to Relution directly. The XML file must first be converted into a binary file; this is explained in the following sections.
Xml file
The WDAC policy xml file contains two pieces of information that are critical to successfully applying the configuration to the Windows devices via Relution.
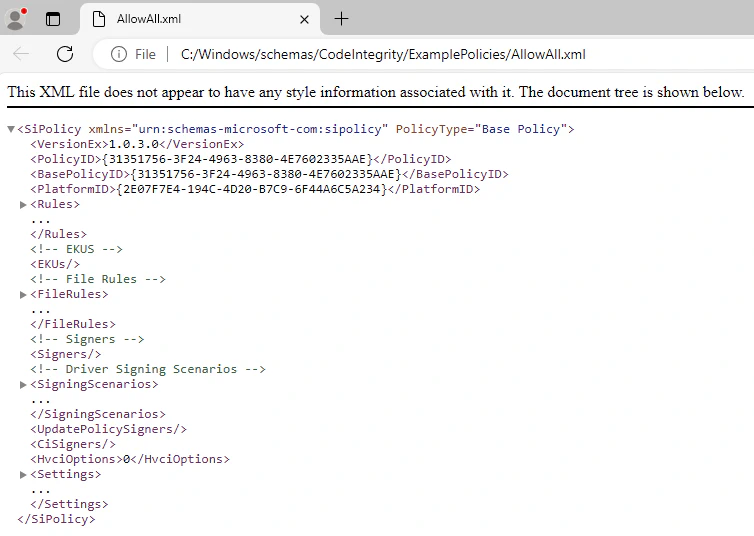
The <PolicyID> is a GUID that uniquely identifies this WDAC policy. It is therefore used for applying, updating and deleting the configuration.
The <VersionEx> is used as versioning for the WDAC policy. Therefore, <VersionEx> must be increased for every update of a WDAC policy. If the version is lower than the most recently applied one, Windows rejects the policy and the update of the configuration via Relution fails.
Convert the xml file
The xml file must be converted into a binary file. This can be done using the ConvertFrom-CIPolicy → PowerShell command.
Example:
ConvertFrom-CIPolicy -XmlFilePath .\AllowAll.xml -BinaryFilePath .\AllowAll.bin
The resulting binary file can be uploaded to Relution in the App Control configuration.
App Control configuration
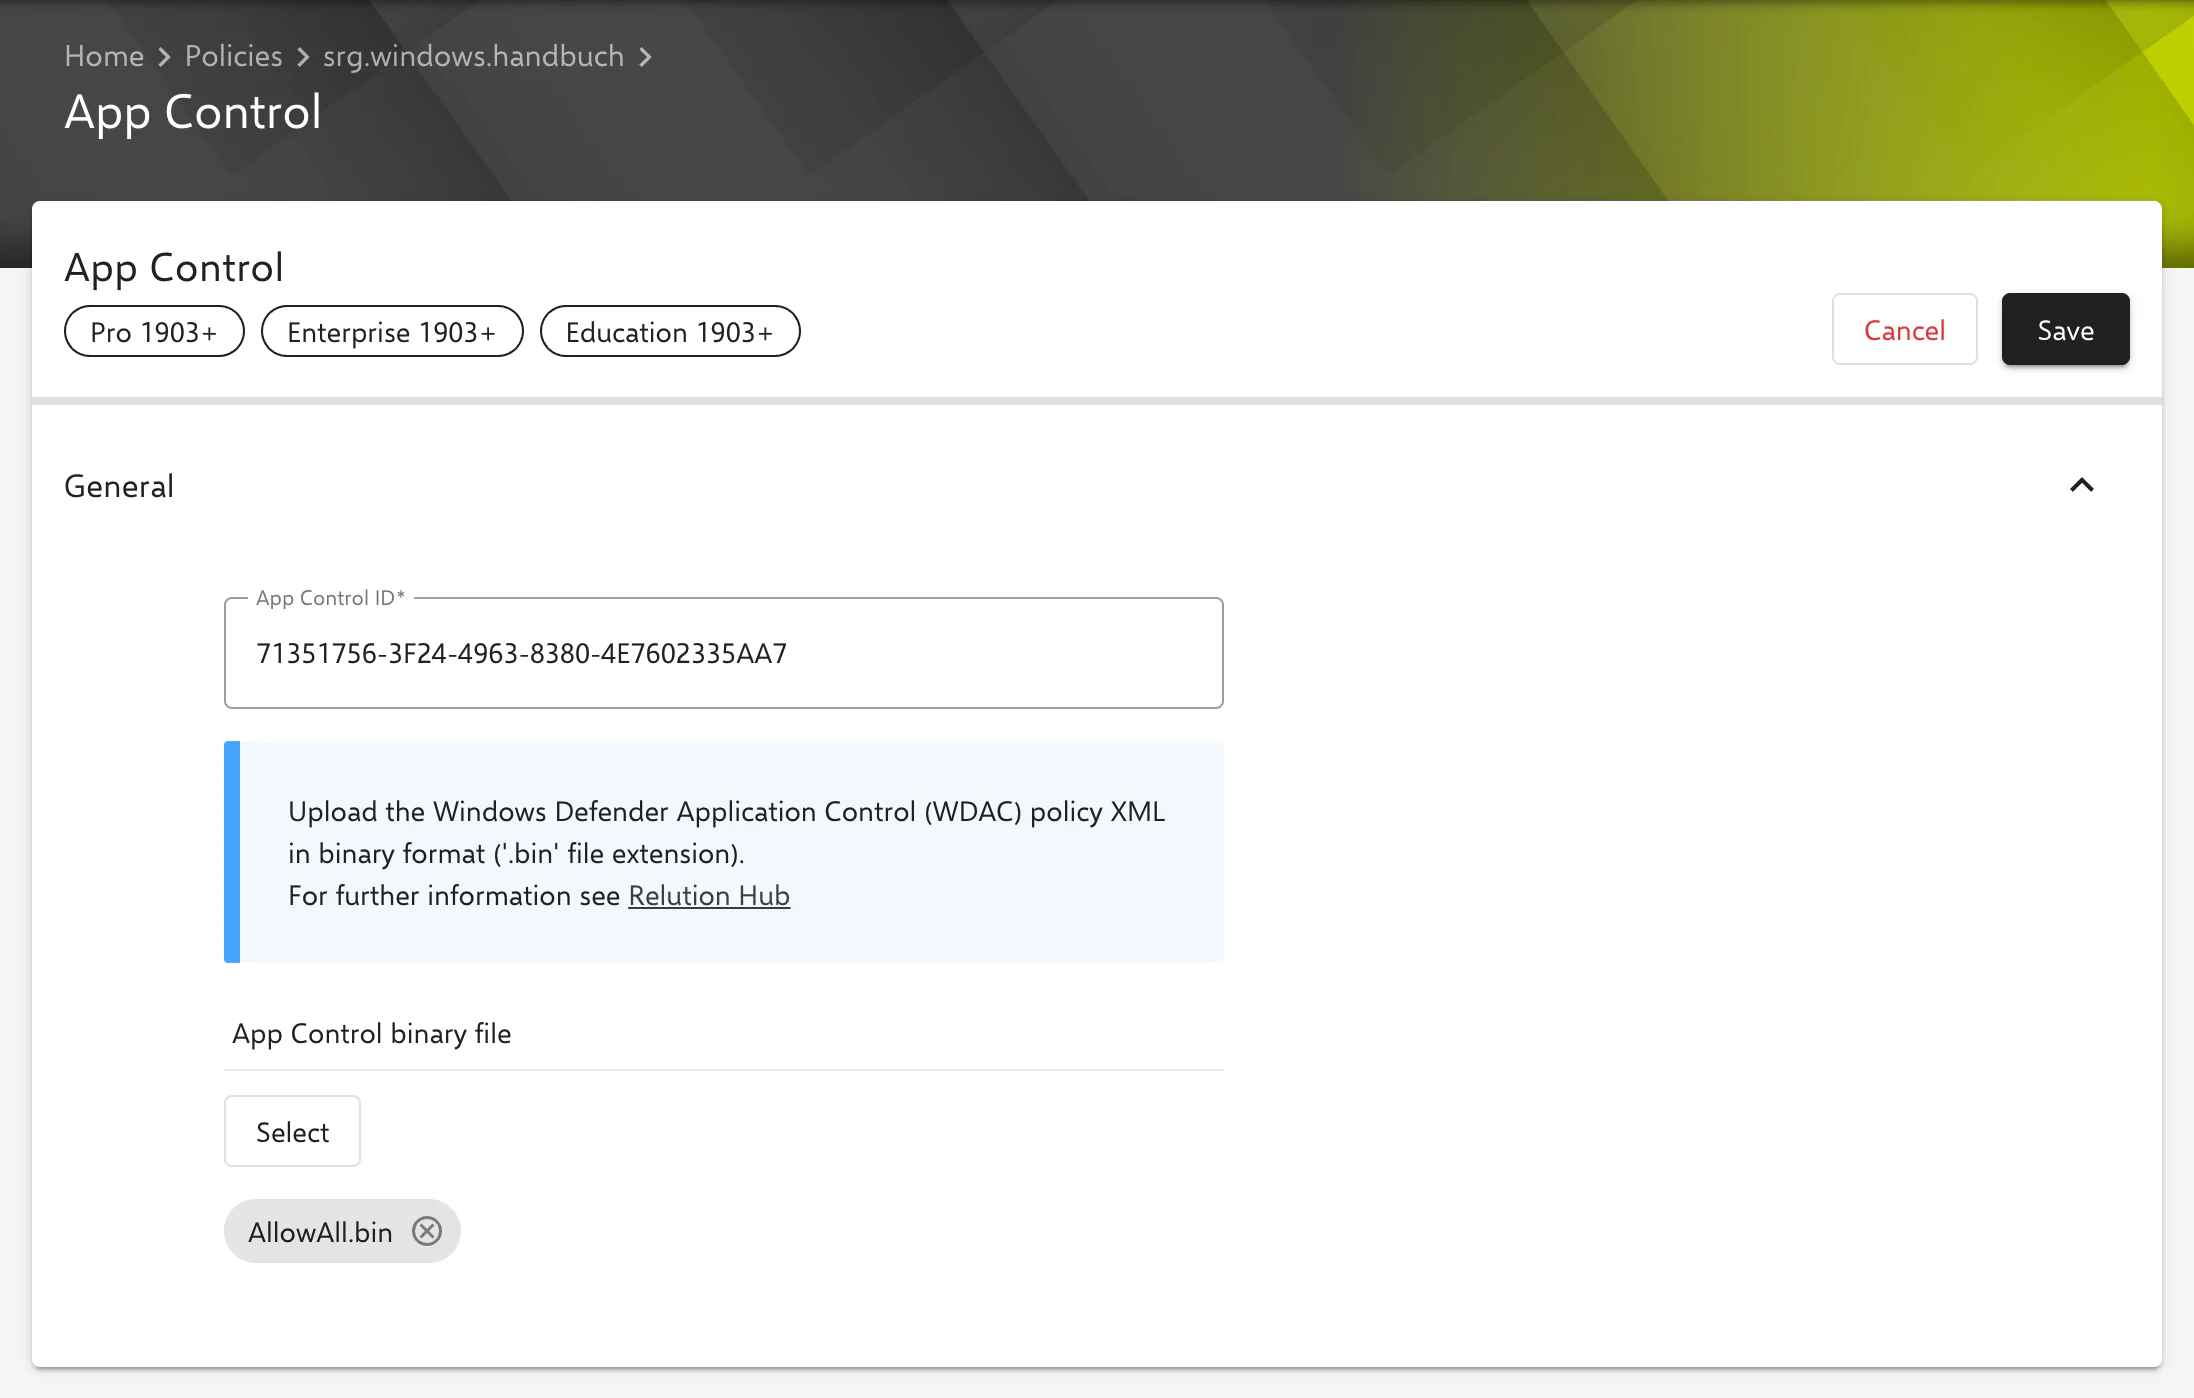
The App Control configuration consists of two mandatory fields:
- Field App Control ID:
For the configuration to be successfully applied to the device, the App Control ID must contain the same value as the
<PolicyID>from the WDAC policy, but without the curly brackets. A GUID in the formatXXXXXXXX-XXXX-XXXX-XXXX-XXXXXXXXXXXXis expected; other input is marked as invalid.- Example:
- PolicyID in WDAC policy:
<PolicyID>{31351756-3F24-4963-8380-4E7602335AAE}</PolicyID> - App Control ID in configuration:
31351756-3F24-4963-8380-4E7602335AAE
- PolicyID in WDAC policy:
- It is not possible to change the entered App Control ID after saving for the first time. However, it is possible to create several (complementary) App Control configurations and apply them to one device.
- Example:
- Field App Control binary file: upload of the WDAC policy in binary format, see WDAC policy generation →. The note in the form mentions the
.binfile extension. Relution does not check the extension, however, so the CIP file of the WDAC Wizard can also be uploaded without renaming it.
Update
In order for a new version of the App Control configuration to be successfully applied to the device, the <PolicyID> in the WDAC policy must have the same value as the App Control ID of the configuration and the <VersionEx> must have a value higher than in the previous version.
Delete
In order for deleting a WDAC policy to be applied to the device, a device restart is required.
Microsoft recommends a workaround so that the app restrictions are removed without restarting, see Microsoft documentation →.
Delete an unsigned application control configuration
In Relution, removal without restarting can be implemented as follows:
- Creation of an Allow-All WDAC policy
- The
<PolicyID>must match the App Control ID - The
<VersionEx>must be higher than the previous version
- The
- Conversion of the XML file into the required binary format
- Creation of a new policy version in Relution
- Upload of the new binary file of the Allow-All WDAC policy to the App Control configuration
- Publication of the new policy version
- This removes the existing restrictions from the device
- Removal of the policy from the device
- This deletes the App Control configuration from the device. However, this is only active after the restart.
Delete a signed application control configuration
Removing a signed WDAC policy (without requiring a restart) can therefore be implemented in Relution as follows:
- Creation of a signed WDAC policy that allows unsigned WDAC policies
- The
<PolicyID>must match the App Control ID - The
<VersionEx>must be higher than the previous version
- The
- Conversion of the XML file into the required binary format
- Creation of a new policy version in Relution
- Upload of the new binary file of the signed WDAC policy (allowing unsigned WDAC policies) to the App Control configuration
- Publication of the new policy version
- This allows unsigned WDAC policies to be applied on the device
- Delete an unsigned application control configuration →